Security & Privacy
Actively exploited vulnerabilities, patches and breaches, plus practical guides to passwords, passkeys, VPNs and privacy.
 News
WordPress 7.1.4 Security Update: Update Now, CISA Confirms Attacks
WordPress Core 7.1.4 fixes a high-severity, unauthenticated RCE flaw attackers began exploiting within days. CISA added it to its KEV catalog on Nov. 3 — here's what to do now.
 Explainer
What Is a Keylogger? How Keylogger Spyware Works
Keyloggers secretly capture everything you type, from passwords to private messages. Here's how they work, how they spread, and how to detect, remove, and prevent them.
 News
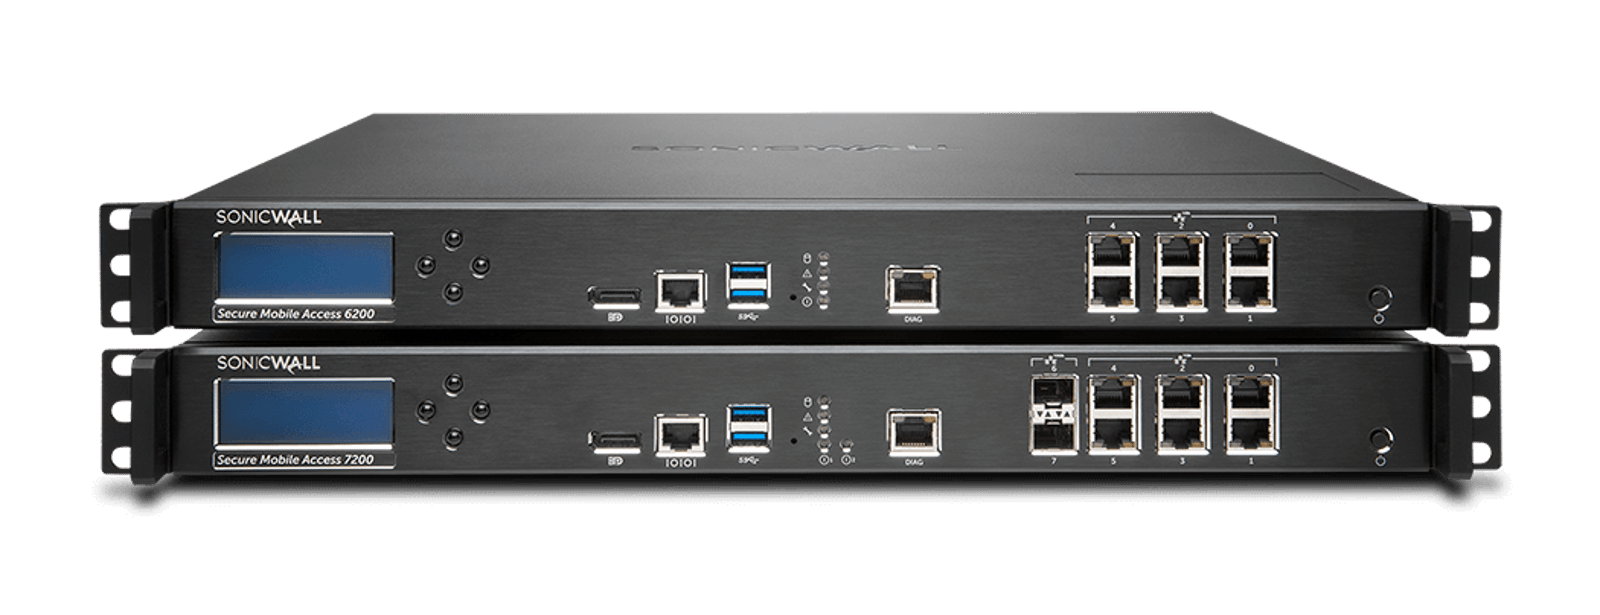
SonicWall Patches Critical CVSS 10.0 SSRF Flaw in SMA1000 VPNs
CVE-2026-102255 lets unauthenticated attackers hijack SMA1000 appliances to reach internal systems. SonicWall says no active exploitation yet; patch before that changes.
 Comparison
Signal vs WhatsApp vs Telegram: Which Is More Secure?
Signal encrypts everything by default, WhatsApp does too but is owned by Meta, and Telegram only encrypts opt-in Secret Chats. Here is the real difference.
 News
Nextcloud CVE-2026-110447: Patch the CODE Server Now
An unauthenticated command injection in Nextcloud's bundled Collabora CODE server is on CISA's KEV list, with attackers planting PHP web shells since September.
 Explainer
Advanced Persistent Threat (APT) Explained: Definition and Lifecycle
APTs are not smash-and-grab malware. They are patient, often state-backed campaigns built to stay hidden inside one target network for months while they move laterally and exfiltrate data.
 News
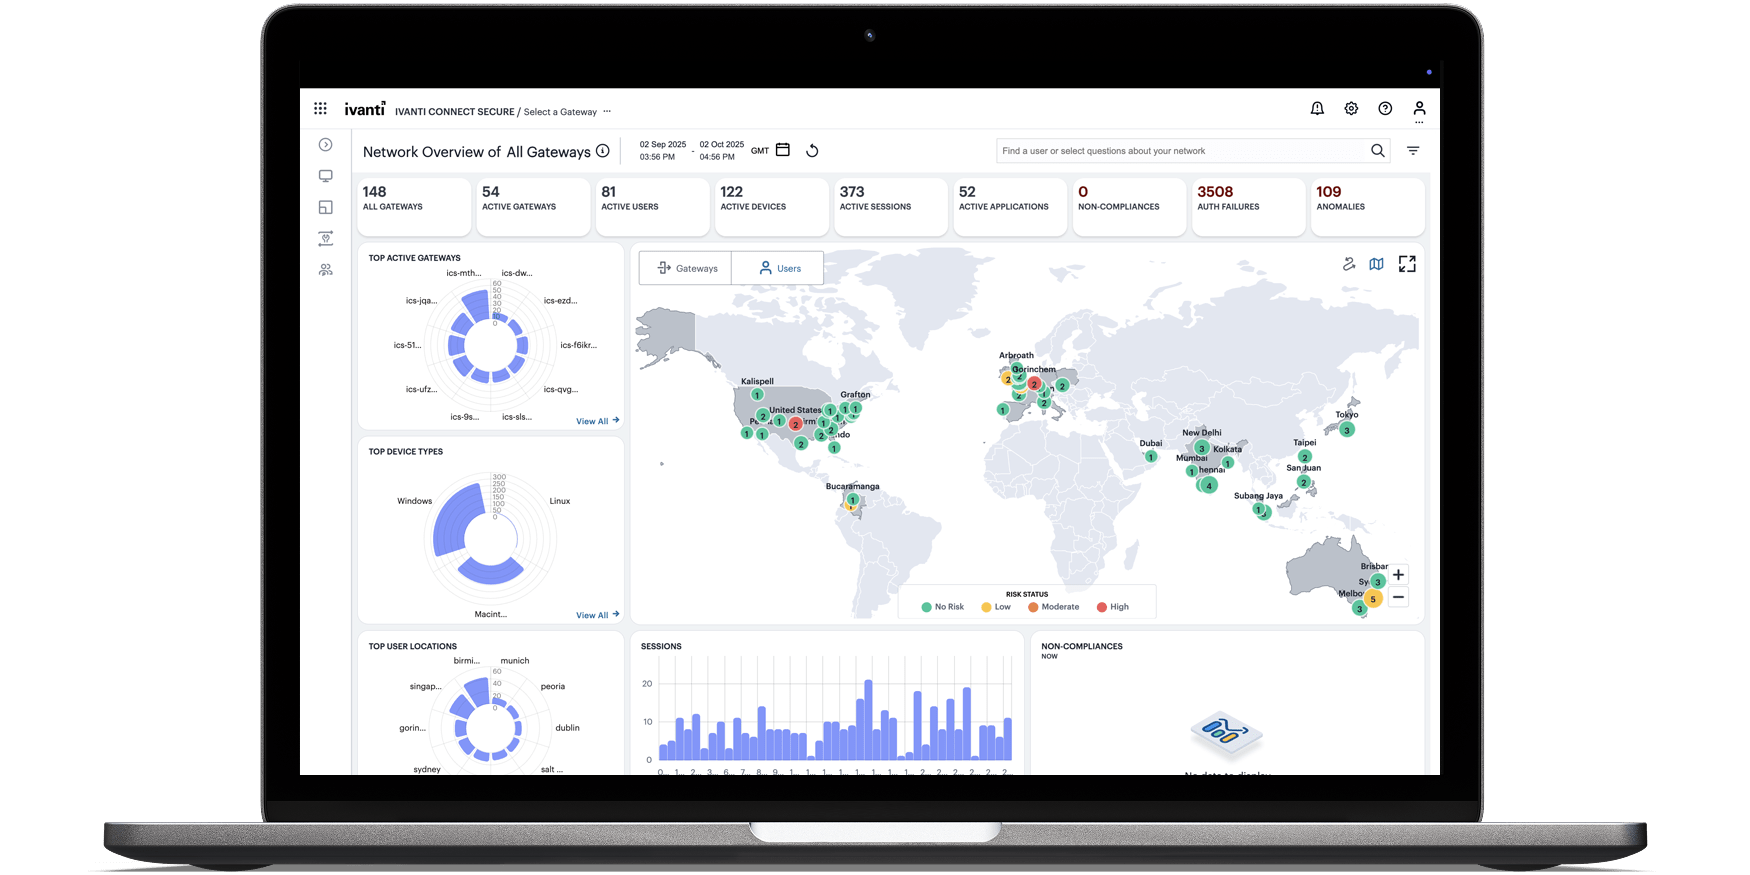
Ivanti Connect Secure CVE-2026-111357, CVE-2026-118527: Patch Now
CISA added two new Ivanti Connect Secure CVEs to its KEV catalog on October 30, separate from October's zero-day, with a federal patch deadline today.
 Comparison
Proton Drive vs Google Drive: Which Is More Private in 2026?
Both store your files in the cloud, but only one says it can't read them. Here's how Proton Drive's zero-access encryption stacks up against Google Drive's standard model.
 News
GitLab RCE Flaw CVE-2026-97229 Now Under Active Attack, CISA Warns
CISA confirms GitLab's maximum-severity CI/CD flaw is under active attack, adding it to the KEV catalog with a federal remediation deadline that has already passed.
 Explainer
What Is Business Email Compromise? BEC Scams Explained
BEC scams impersonate executives, vendors and partners to trick employees into wiring money — and they cost reported victims over $3 billion in 2025 alone.
 News
VMware vCenter RCE Flaw CVE-2026-59310: Patch Now
A critical, unauthenticated directory-traversal flaw in vCenter's Syslog server is being actively exploited for remote code execution. Broadcom has no workaround.
NordVPN vs Proton VPN: Price, Speed and Privacy Compared
NordVPN brings more servers and bundled extras. Proton VPN brings Swiss jurisdiction and open-source apps. Here is how their price, speed and privacy claims compare.
 News
PHP RCE Flaws CVE-2026-109618, 109619: Patch Now
Two critical PHP engine flaws, CVE-2026-109618 and CVE-2026-109619, are now listed as actively exploited by CISA. Patch to 8.2.35, 8.3.36, 8.4.27 or 8.5.12 now.
 Explainer
What Is a Botnet? How It Works and How to Stay Safe
Botnets quietly turn ordinary routers, cameras and computers into an attacker's army. Here's how devices get recruited, what they're used for, and how to stay safe.
 News
Brotli Flaw Now Under Active Attack: Patch Node.js and .NET
CSA rates the Brotli decoder bug CVSS 9.8 with a public PoC and reports of active exploitation, now confirmed to also affect Microsoft .NET, not just Node.js.
 Explainer
What Is Credential Stuffing? How It Works and How to Stop It
Credential stuffing reuses passwords leaked in one breach to break into unrelated accounts elsewhere — here is how it works and how to stop it.
 Comparison
Surfshark vs ExpressVPN: Price, Speed, and Privacy Compared
Both now sell AI and identity bundles, not just tunnels. Here is how Surfshark's Dausos and ExpressVPN's Lightway compare on price, devices, and audited privacy claims.
 News
VMware ESX Logging Flaw CVE-2026-41709: Patch Now
CISA flagged a VMware ESX logging gap as actively exploited on October 28, with a November 11 federal deadline. Here's what's affected and how to fix it.
 Explainer
What Is Post-Quantum Cryptography? PQC Standards Explained
NIST has finalized its quantum-resistant encryption standards. Here's what ML-KEM, ML-DSA and SLH-DSA actually do, who's deployed them, and what to do now versus later.
 News
Plex2Shell Flaws Let Hackers Hijack Plex Servers: Patch Now
Four chained vulnerabilities dubbed Plex2Shell let attackers hijack unpatched Plex Media Server installs. CISA added them to its KEV catalog on October 20.
 Comparison
Duo Mobile vs Microsoft Authenticator: Which Should You Use?
Both apps approve sign-ins with a tap, but Duo Mobile and Microsoft Authenticator differ sharply on pricing, admin controls and which systems they protect.
 News
Cisco ASA FTD VPN Flaw CVE-2026-76418 Patch Now
Cisco confirms active exploitation of an unauthenticated VPN flaw that can crash ASA and FTD firewalls. CISA set a November 1 deadline. Here's what to patch and how.
 Explainer
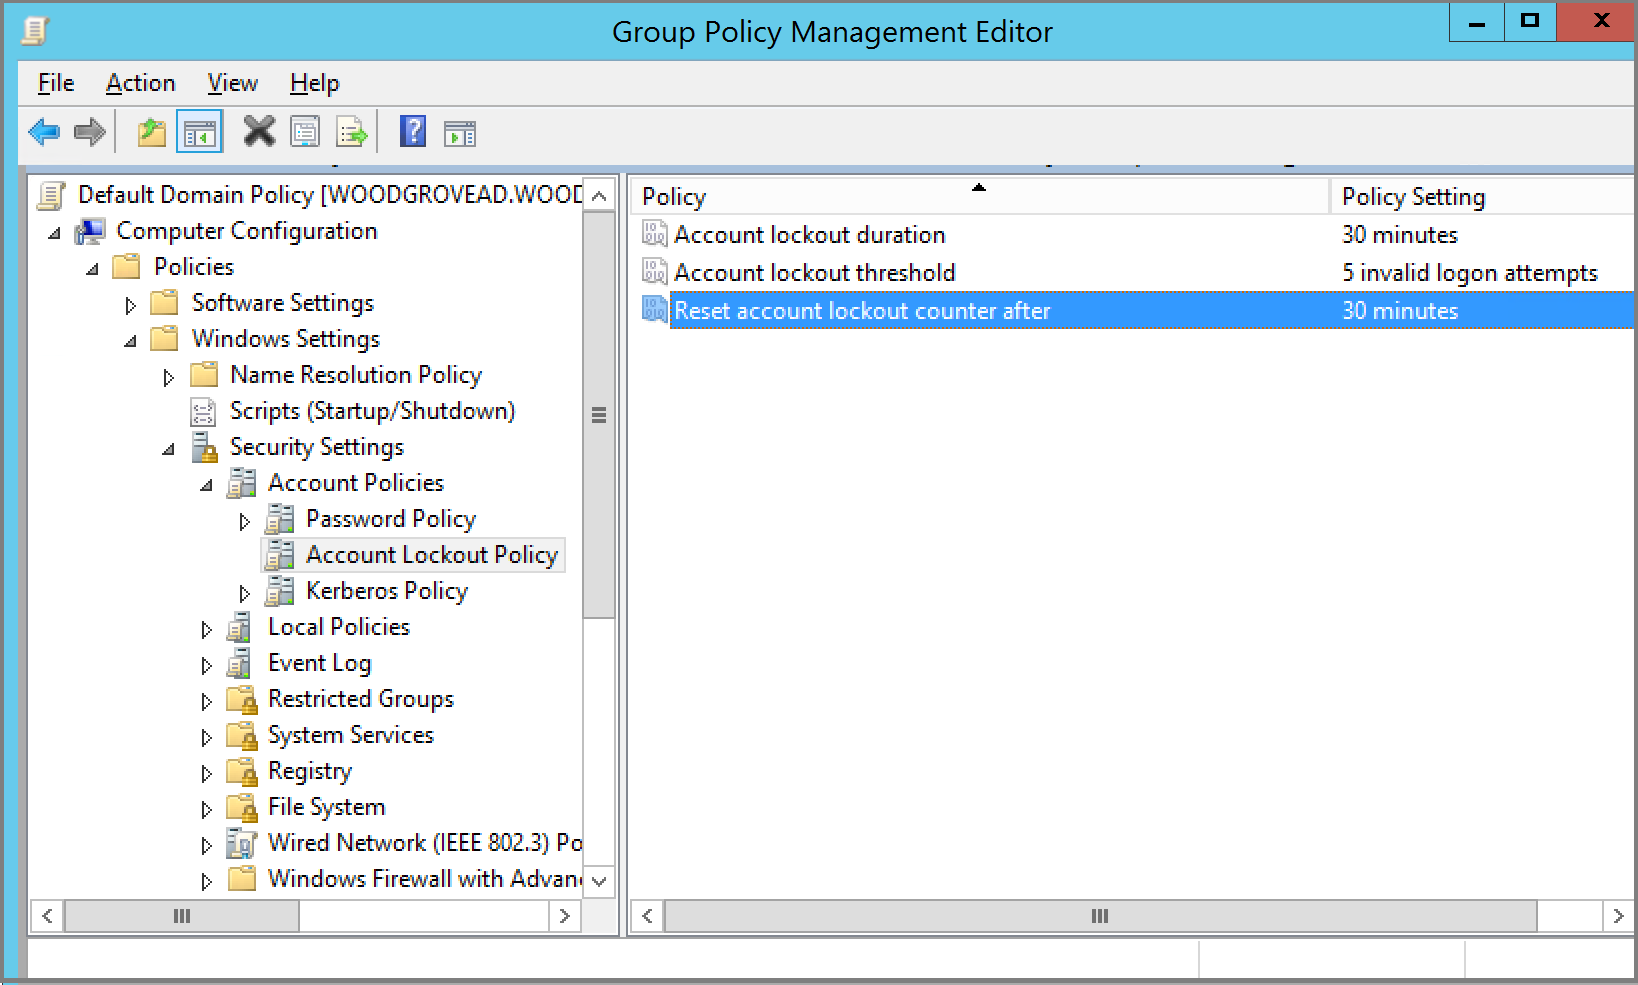
What Is a Brute Force Attack? How It Works and How to Stop It
Attackers throw millions of password guesses at your accounts every second. Here's how brute force attacks work, how they differ from credential stuffing, and what actually stops them.
 News
CISA Flags Fragnesia (CVE-2026-46300) Linux Flaw: Patch Now
A logic bug in the Linux kernel's XFRM ESP-in-TCP code lets a local user write to read-only files and gain root. CISA added it to KEV; a Metasploit module already exists.
 Comparison
1Password vs Bitwarden: Price, Passkeys, and Security Compared
Bitwarden undercuts 1Password on price and offers a real free plan, while 1Password adds polish and enterprise SSO, but both now store and autofill passkeys.
 News
Oracle E-Business Suite Vulnerability: Critical Flaw, Patch Now
Oracle’s October 2026 Critical Patch Update fixes an unauthenticated SQL-injection-to-RCE flaw (CVSS 9.8) and a perfect-10.0 bug in E-Business Suite. Here’s what’s affected and how to patch.
 Explainer
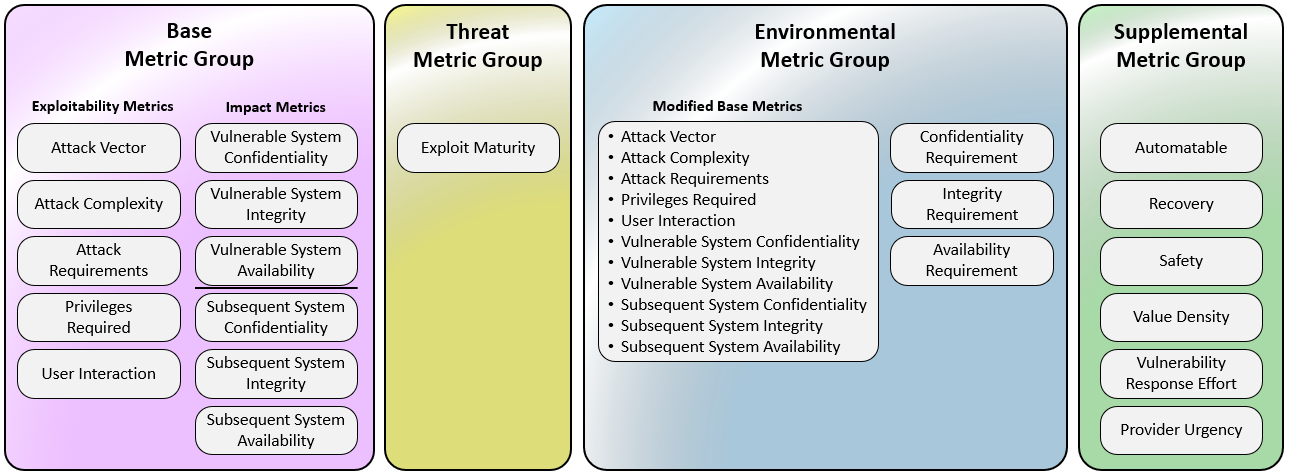
What Is a CVE? How Vulnerability IDs and CVSS Scores Work
What a CVE identifier actually is, who assigns it, how CVSS severity bands work, and how CISA's KEV catalog helps you decide how urgently to patch.
 News
Microsoft Authenticator Flaw Let Apps Steal Work Tokens: Update Now
CVE-2026-80097 let a permission-less Android app pose as Teams and steal Microsoft Authenticator tokens. Here's what happened and how to update.
 Comparison
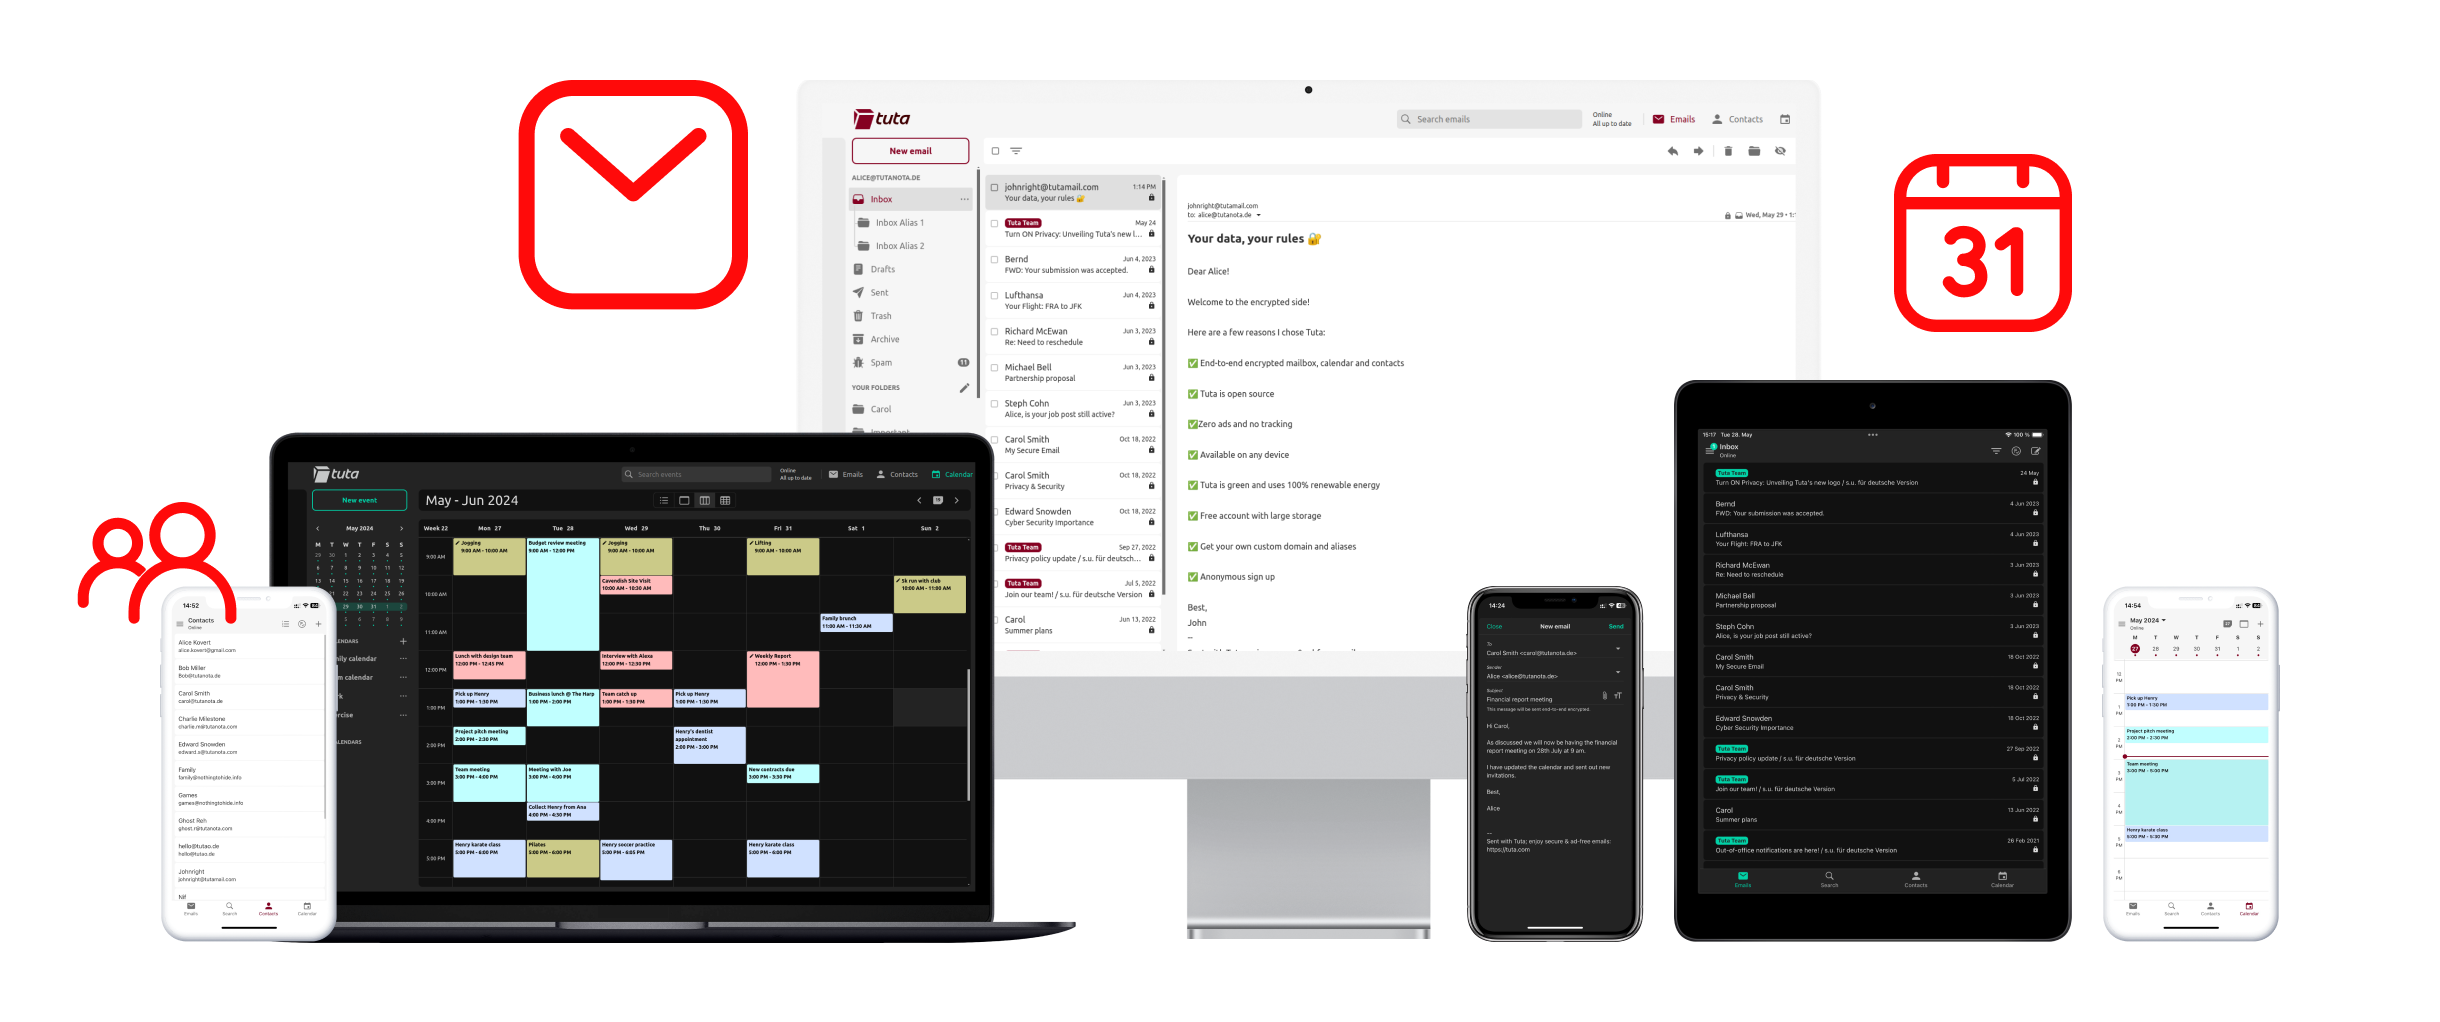
Proton Mail vs Tuta: Which Encrypted Email Should You Use in 2026?
Proton Mail and Tuta differ sharply on what they actually encrypt, where they're legally based, and what each costs per mailbox.
 News
CISA Flags Critical Adobe Commerce Upload Flaw, Patch Now
CISA confirms active exploitation of a critical Adobe Commerce and Magento Open Source file-upload flaw patched in July, giving federal agencies until November 10 to act.
 Explainer
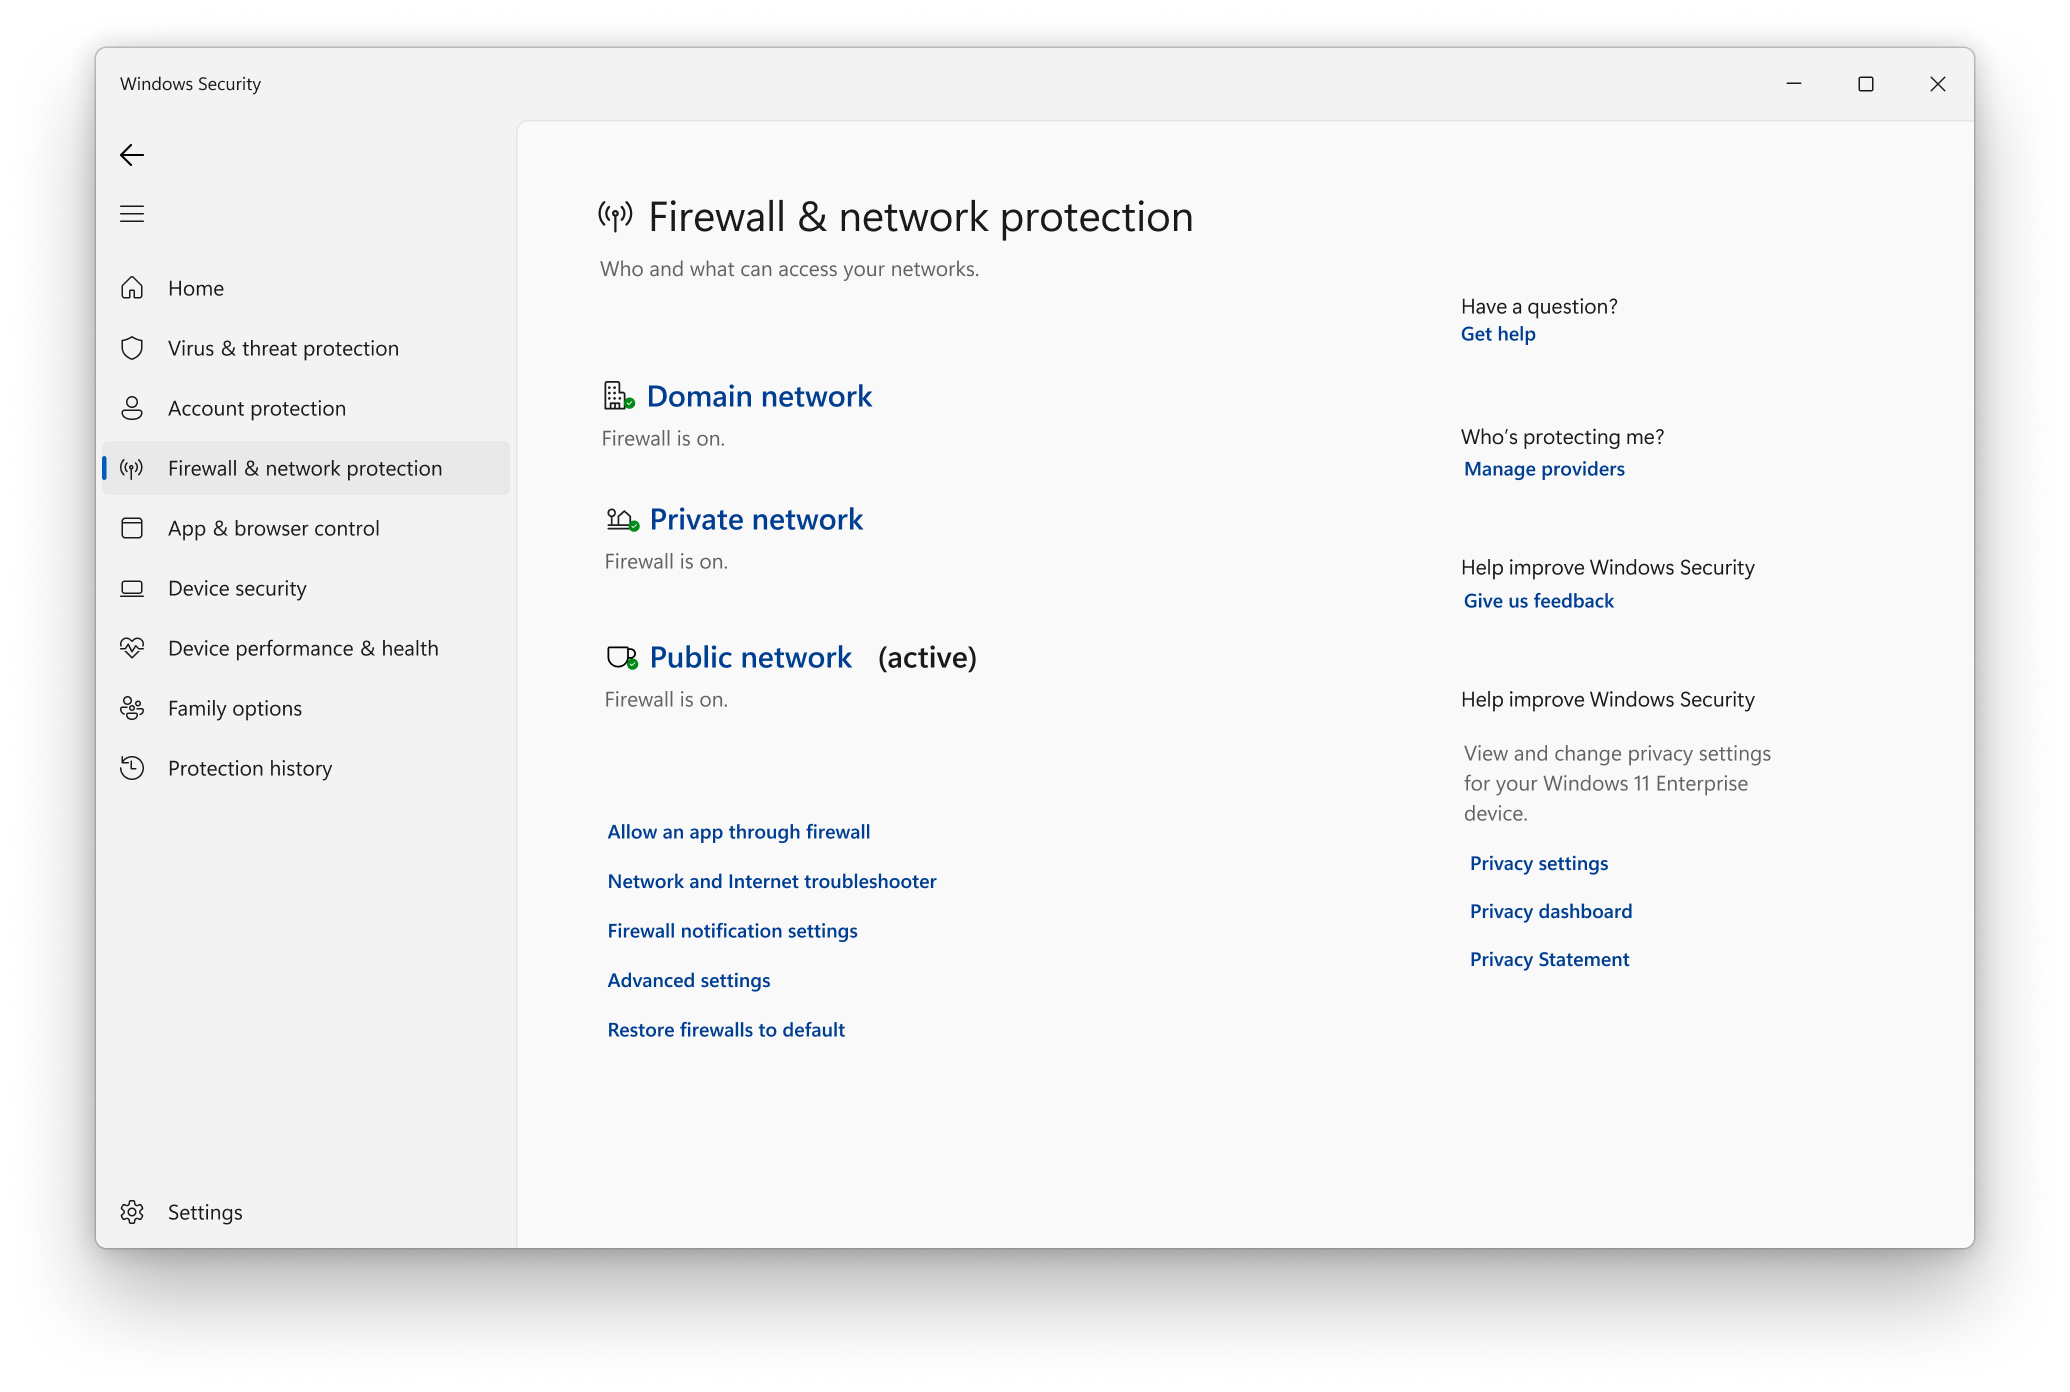
What Is a Firewall and How Does It Work?
A plain-English explainer on what a firewall is, how it filters traffic, the main types, and why Windows Defender Firewall still matters in 2026.
 News
Nextcloud Vulnerability Lets Hackers Backdoor Servers: Patch Now
A critical command-injection bug in Nextcloud's built-in Collabora CODE server has been exploited since September to plant web shells and steal credentials.
 Comparison
Brave vs Firefox: Which Is the Better Privacy Browser in 2026?
A privacy-and-security comparison of Brave's Shields and farbling against Firefox's tracking protection, containers and new built-in VPN in 2026.
 News
Arista VeloCloud Orchestrator Zero-Day Is Being Exploited: Patch Now
A critical SQL injection flaw lets a low-privilege VeloCloud Orchestrator user become a superuser. Arista says it is already being exploited, and CISA has set a patch deadline.
What Is a Supply Chain Attack? How It Works and How to Stay Safe
What a supply chain attack is, how attackers exploit trusted vendors and dependencies, and the defenses organizations use to stop them.
PHP2Shell Attacks Are Underway: What Unpatched Servers Face Now
Days after PHP patched two critical php2shell RCE flaws, Sophos, Tanium and watchTowr report real exploitation attempts against unpatched servers.
 Comparison
Proton VPN vs Mullvad: Price, Speed and Privacy Compared
Proton VPN and Mullvad are two of the most privacy-focused VPNs on the market. Here is how their official pricing, server networks, protocols, audits and payment-privacy options compare.
 News
eMudhra CA Key Compromise: What Happened and What It Means
Eight eMudhra certificate authority keys were so weak they could be reconstructed by guesswork, not stolen. Browsers blocked them within a day — here's what happened and who's at risk.
 Guide
What Is SIM Swapping? How the Scam Works and How to Stop It
SIM swapping lets a scammer hijack your phone number to intercept the SMS codes meant to protect your accounts. Here's how the scam works, the warning signs, and how to lock it down.
 News
PHP Ships Emergency Patches for Critical PHP2Shell RCE Flaws
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 fix two critical, unauthenticated RCE flaws rated CVSS 9.2 that hit almost every PHP web server. Patching is the only real fix.
 Guide
What Is a VPN Kill Switch? How It Works and How to Test It
A VPN kill switch cuts your internet the instant the VPN disconnects, so your real IP and DNS never leak. Here is how it works, how to enable it, and how to test it.
 News
Loblaw Data Breach: 2 Million Canadians Affected, What to Do Now
Loblaw disclosed on October 23, 2026 that the March data breach affected about 2 million Canadians, exposing contact, loyalty and partial payment data.
 Comparison
Bark vs Life360: Content Monitoring or Location Tracking?
Bark flags risky texts, social media and content; Life360 tracks real-time location and driving safety. Here is how their pricing and features actually compare.
 News
CISA, FBI Warn SafePay Ransomware Has Hit 600+ Organizations
A joint advisory from CISA, the FBI and international partners details how SafePay ransomware has breached 600+ organizations since August 2024, and how to defend against it.
 Explainer
What Is Juice Jacking? The Airport USB Charging Risk, Explained
Public USB charging ports can carry malware along with power. Here's what the risk really looks like in 2026, and how to protect your phone without giving up a charge.
 News
Quest Diagnostics Data Breach: What We Know About the Quanum Hack
Quest Diagnostics says an unauthorized party accessed patient records through its Quanum LSM ordering portal. The company has not yet said how many patients are affected.
 Comparison
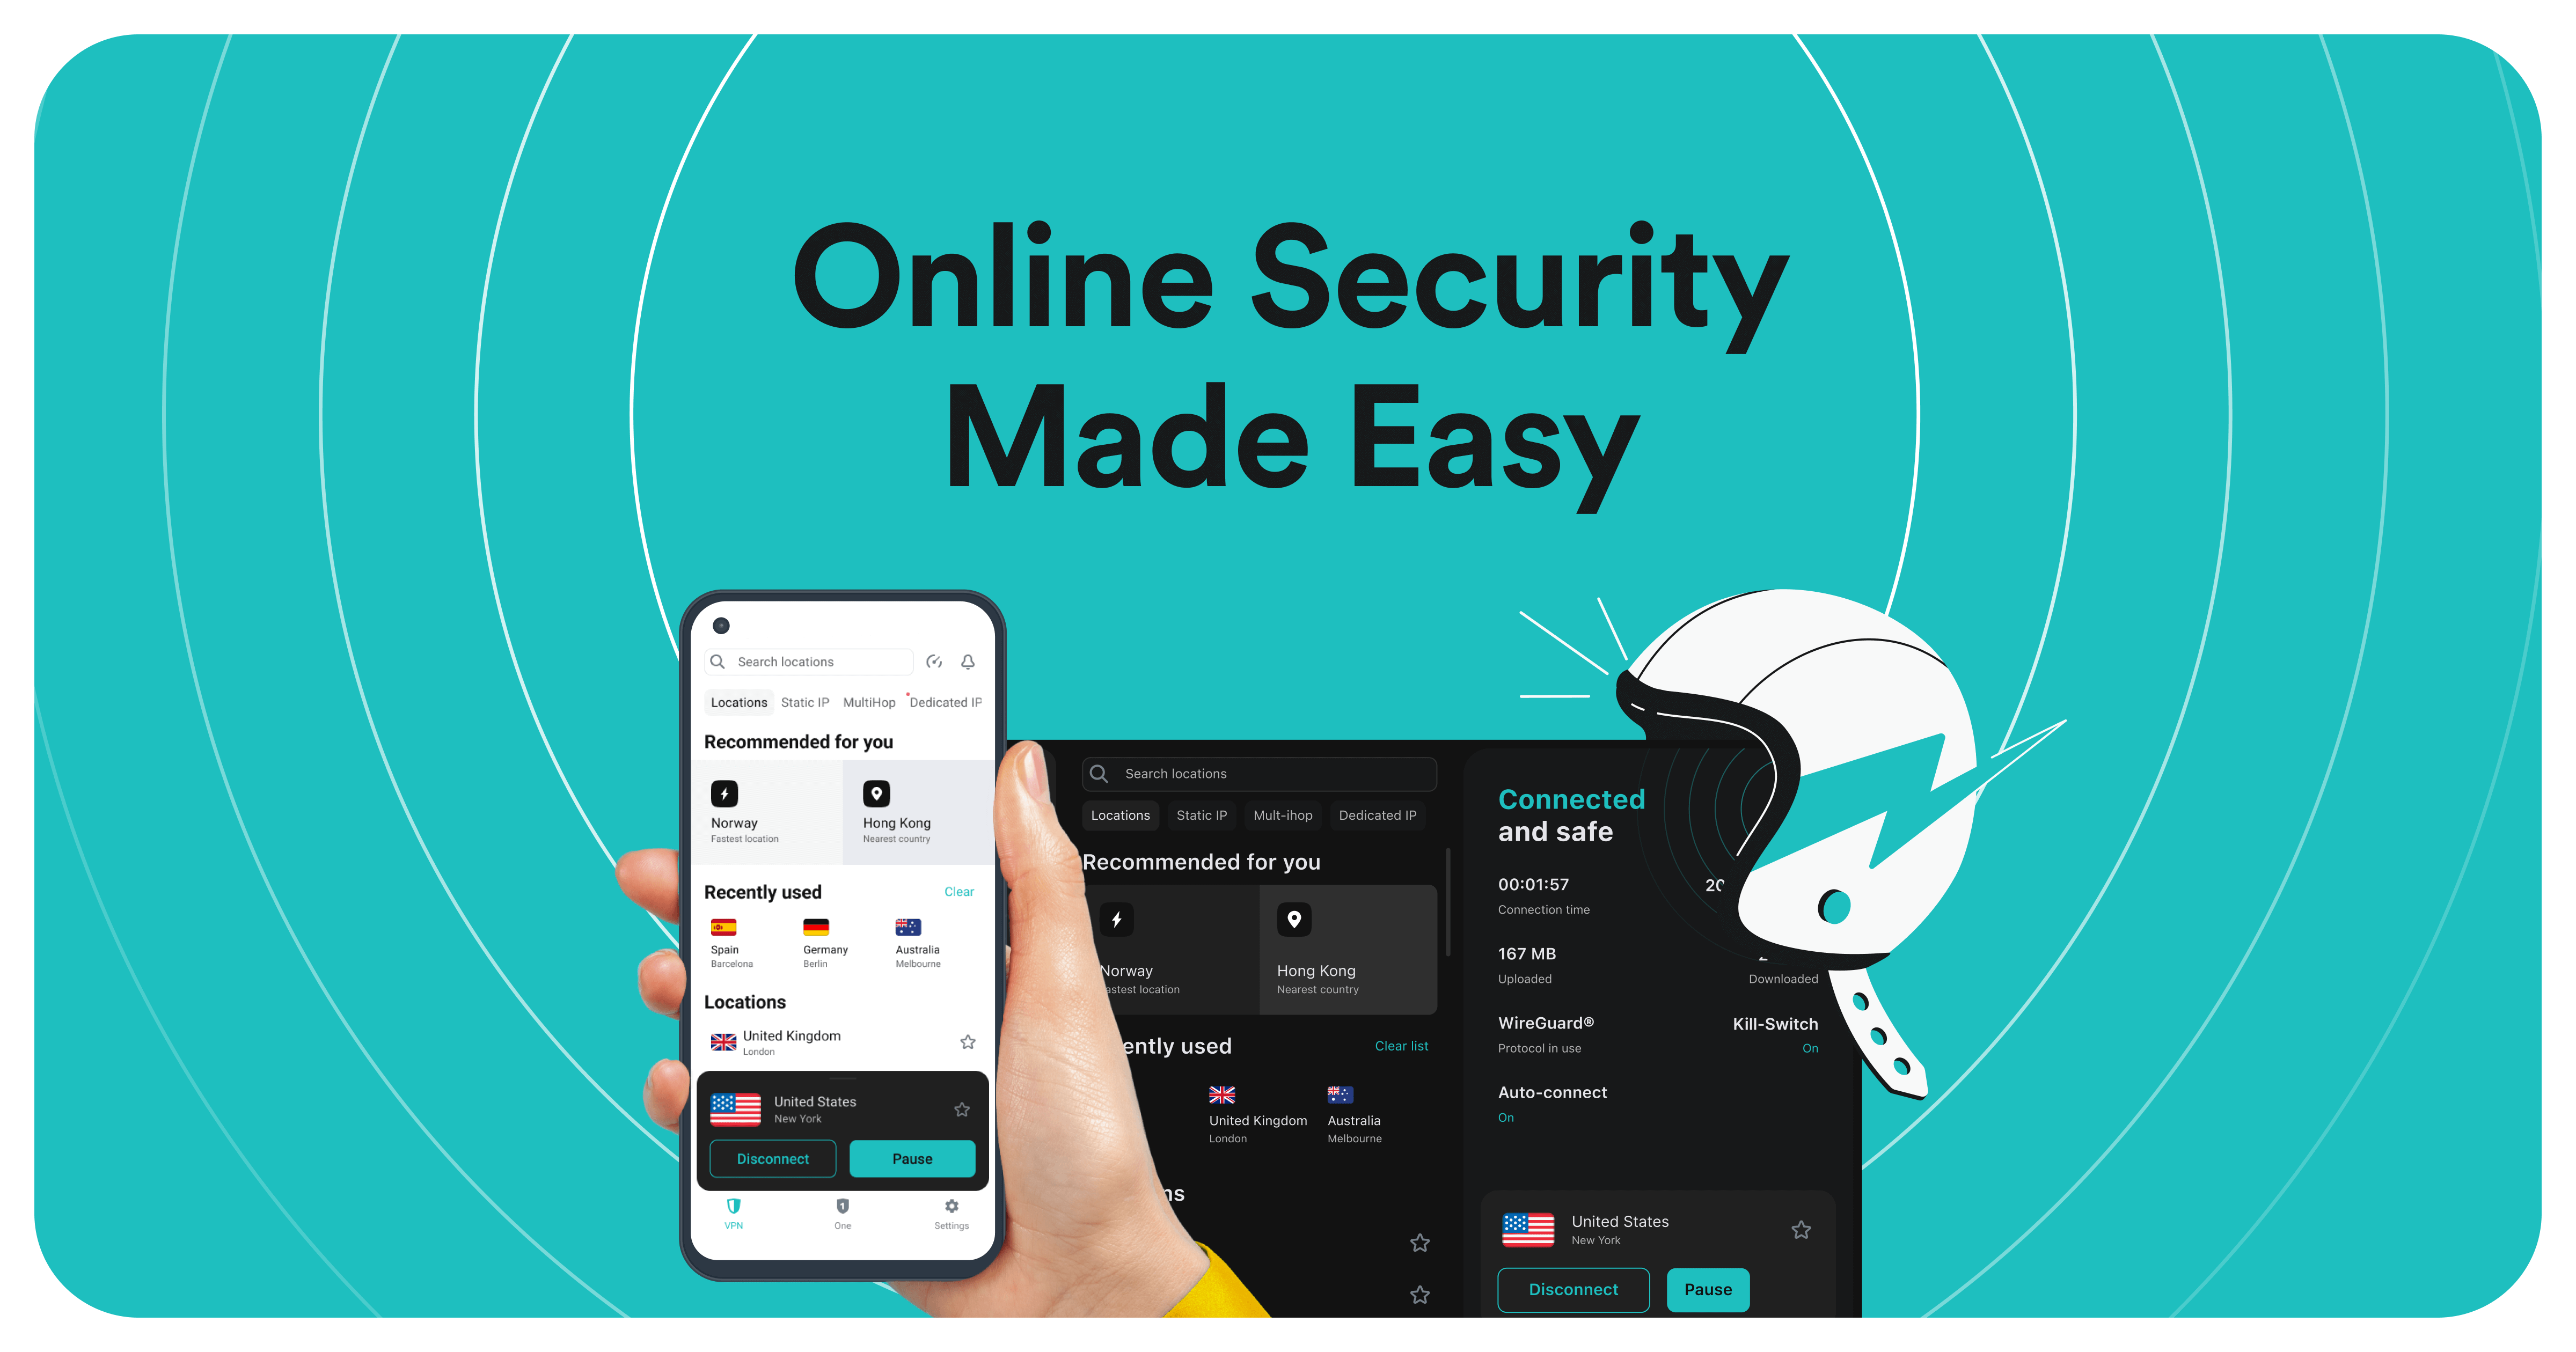
NordVPN vs. Surfshark: Price, Devices, and Security Compared
Surfshark is cheaper with unlimited devices; NordVPN has more servers and a longer audited no-logs track record. Here's how they compare, tier by tier.
 News
Capcom Data Breach: 11.7 Million CAPCOM ID Accounts Exposed
Capcom says unauthorized access exposed email addresses and account data for 11,774,247 CAPCOM ID users, with 196 accounts having passwords changed without permission.
 Explainer
What Is Prompt Injection? How AI Agents Get Hijacked
Hidden instructions in an email or webpage can hijack an AI agent. Here is how prompt injection works, why OWASP ranks it the top AI risk, and how to stop it.
 News
Railway Security Breach: What Happened and What to Do Now
Railway disclosed unauthorized access to stored environment variables, paused builds platform-wide, and is telling every user to rotate credentials. Here's the timeline and checklist.
 Comparison
Malwarebytes vs Bitdefender: Pricing, Features and Verdict
Both score a perfect AV-TEST rating in 2026, so the real Malwarebytes vs Bitdefender choice comes down to price, devices and which extras you need.
 News
ETS Data Breach: California Student Data Exposed
A compromised login let an intruder copy California student records from ETS's file-transfer site for months. Here's what was exposed and how to get the free identity protection.
 Explainer
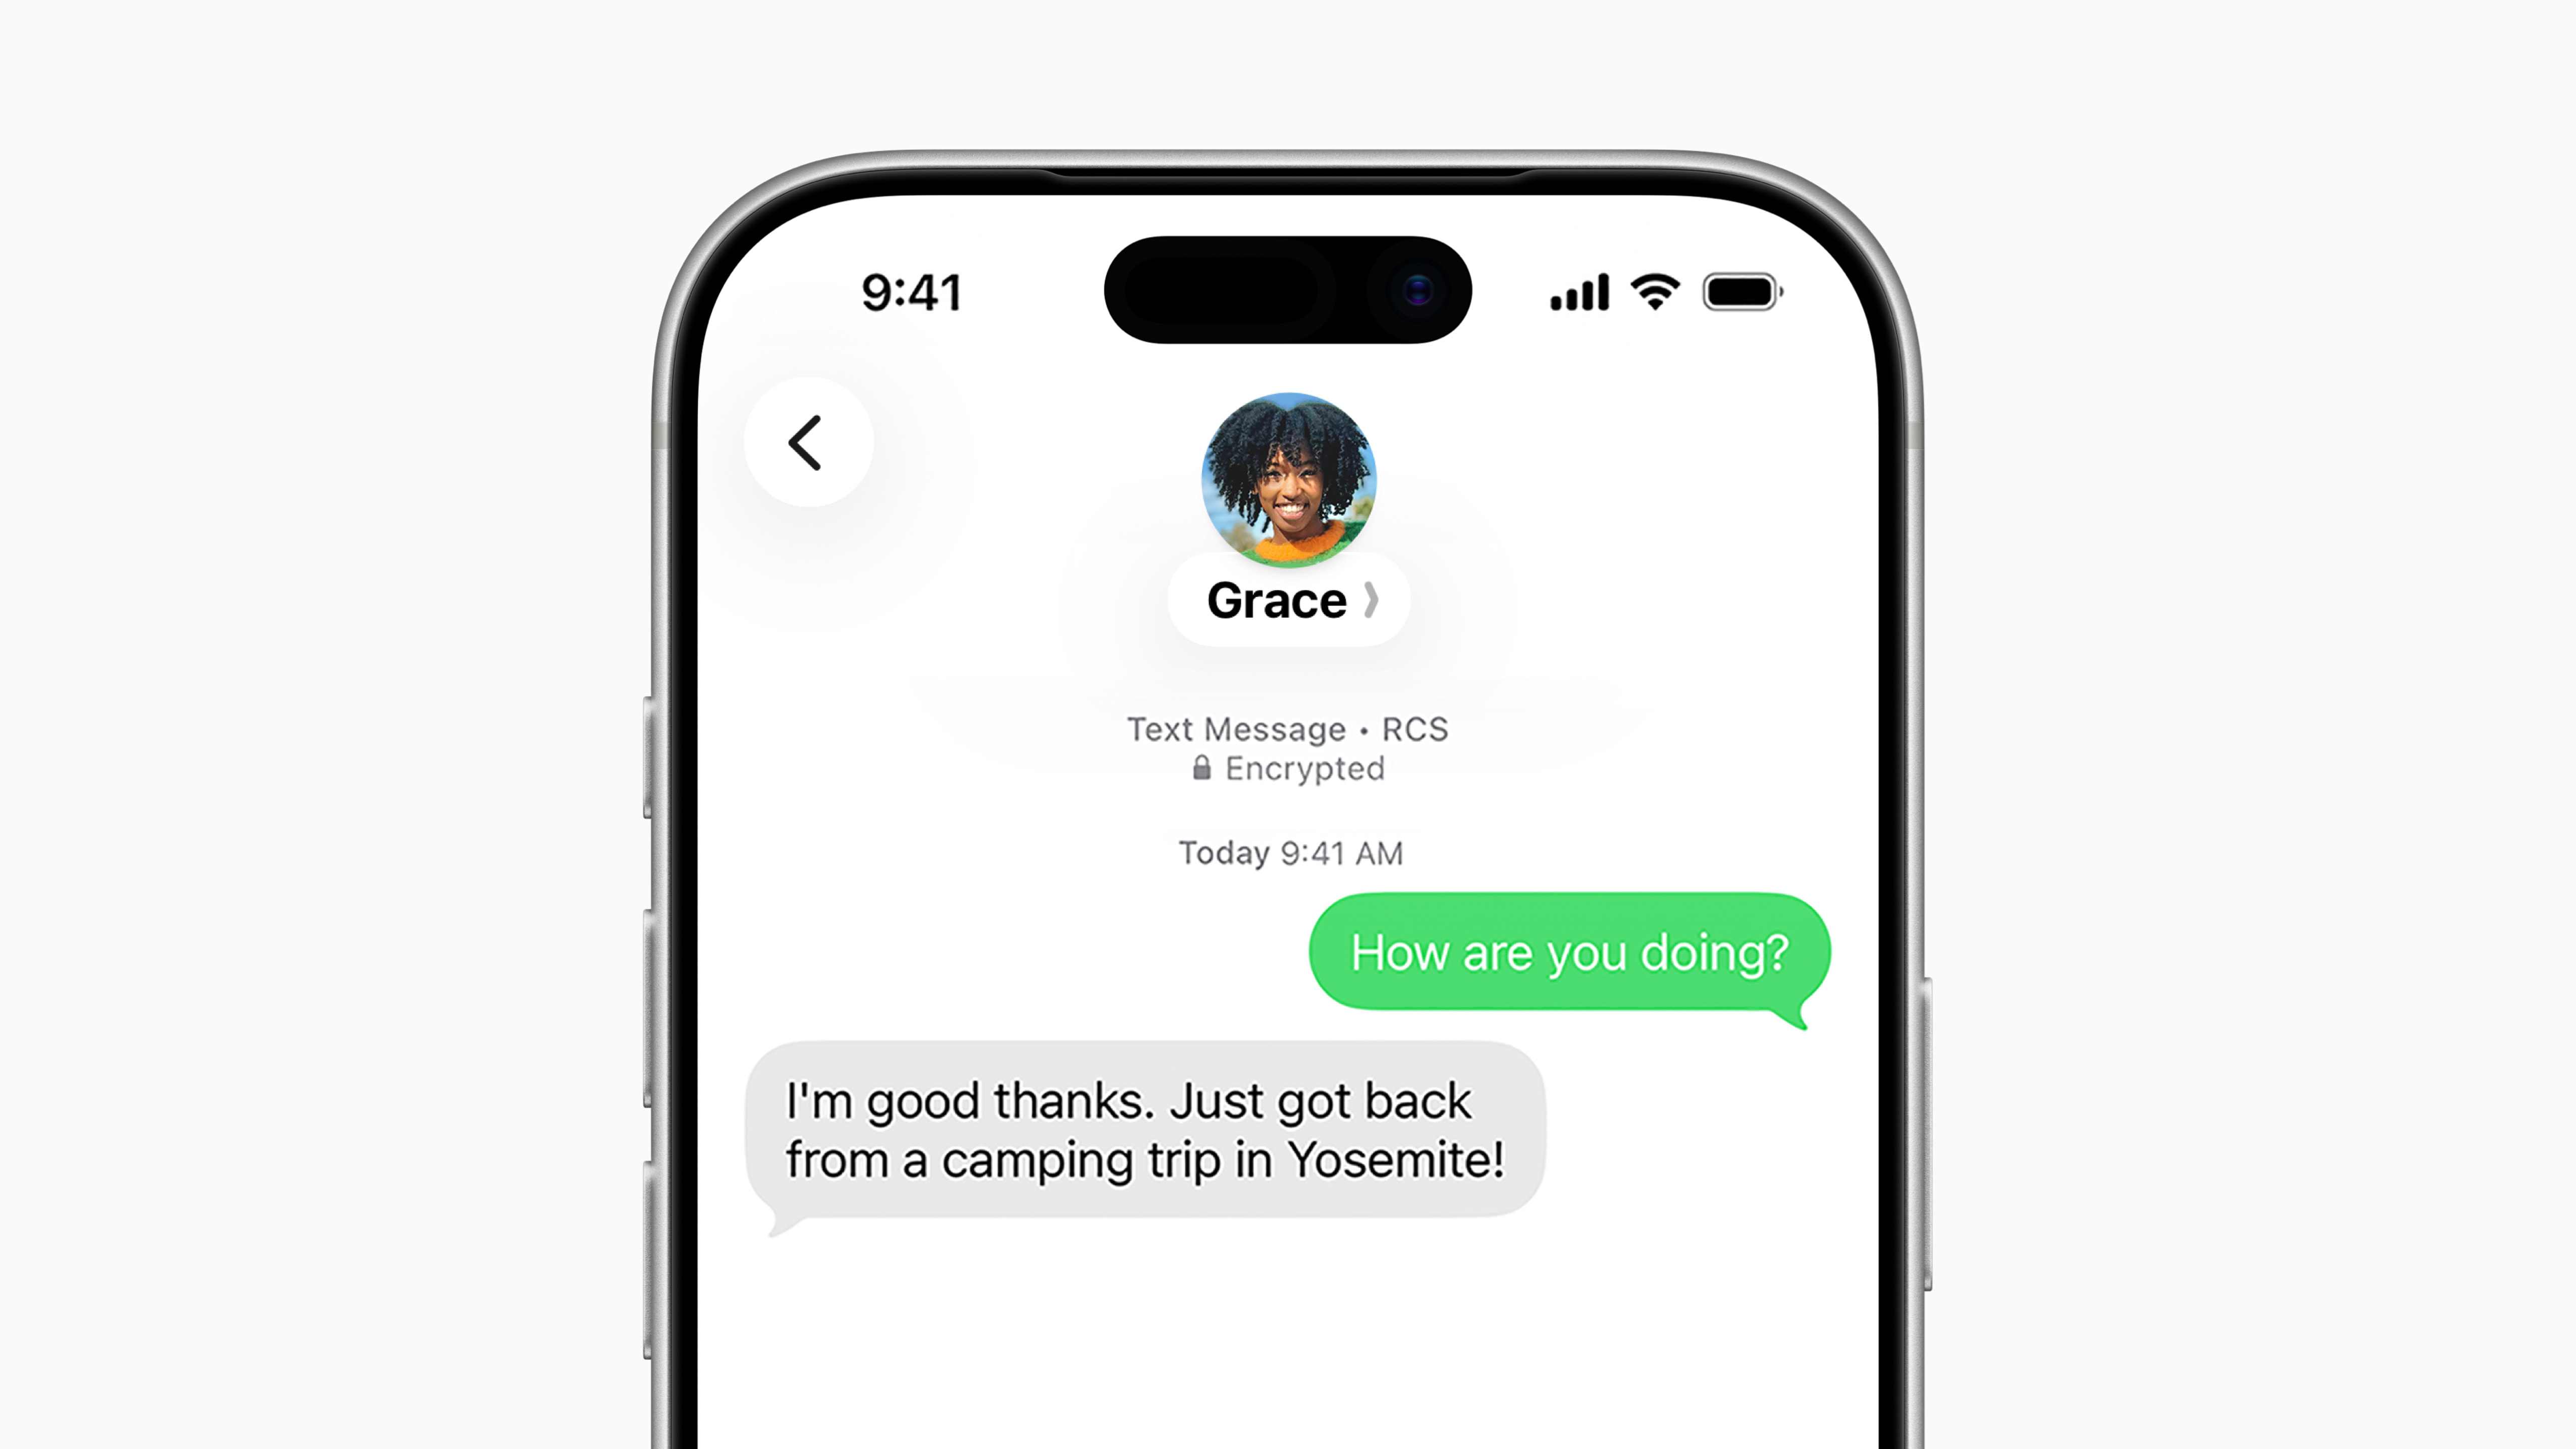
What Is End-to-End Encryption? How It Works and Where It's Used
What end-to-end encryption really means, how the key exchange works, and whether it's actually on by default in WhatsApp, Signal, iMessage and Google Messages.
 News
Burger King Japan Data Breach Exposes 11.18 Million Records
BK Japan says attackers accessed its app membership system for five days in October, exposing data for roughly 11.18 million accounts. Cards and passwords were not affected, the company says.
 Comparison
uBlock Origin vs AdGuard: Which Ad Blocker Should You Use Now?
Chrome removed Manifest V2, crippling uBlock Origin there. Here is how uBlock Origin Lite and AdGuard compare on Chrome, Firefox, Brave, and Safari.
 News
CenterPoint Energy Data Breach: 1,062,060 Texans Affected
A state filing confirms 1,062,060 Texans had Social Security and driver's license numbers exposed in the CenterPoint Energy breach. A hacker's 7.49M-record claim remains unverified.
 Explainer
What Is a DDoS Attack? How It Works and How to Protect Yourself
A DDoS attack uses a botnet of hijacked devices to flood a target with traffic until it buckles. Here's how the three main attack types work and how to lower your risk.
 News
Fake WatchGuard VPN Site Phished MSP Logins, Then Installed Real App
Huntress found a lookalike WatchGuard VPN download site that steals credentials in a browser pop-up, then serves WatchGuard's genuine signed installer, part of the broader Storm-2561 campaign.
 Comparison
Tailscale vs WireGuard: Which Should You Use in 2026?
Tailscale runs on the WireGuard protocol but adds automatic key exchange, NAT traversal, and ACLs. Here is how to choose between them in 2026.
NewsCisco Secure Email Gateway CVE-2026-76519: Patch Now, CISA Warns
A critical, unauthenticated file-write flaw in Cisco Secure Email Gateway's malware scanner is being actively exploited. Here's who's affected and how to patch.
 Explainer
What Is a Man-in-the-Middle Attack and How Do You Stop One?
A man-in-the-middle attack lets an attacker secretly intercept and alter traffic between two parties who believe they're talking directly. Here's how MITM attacks work and how to block them.
 News
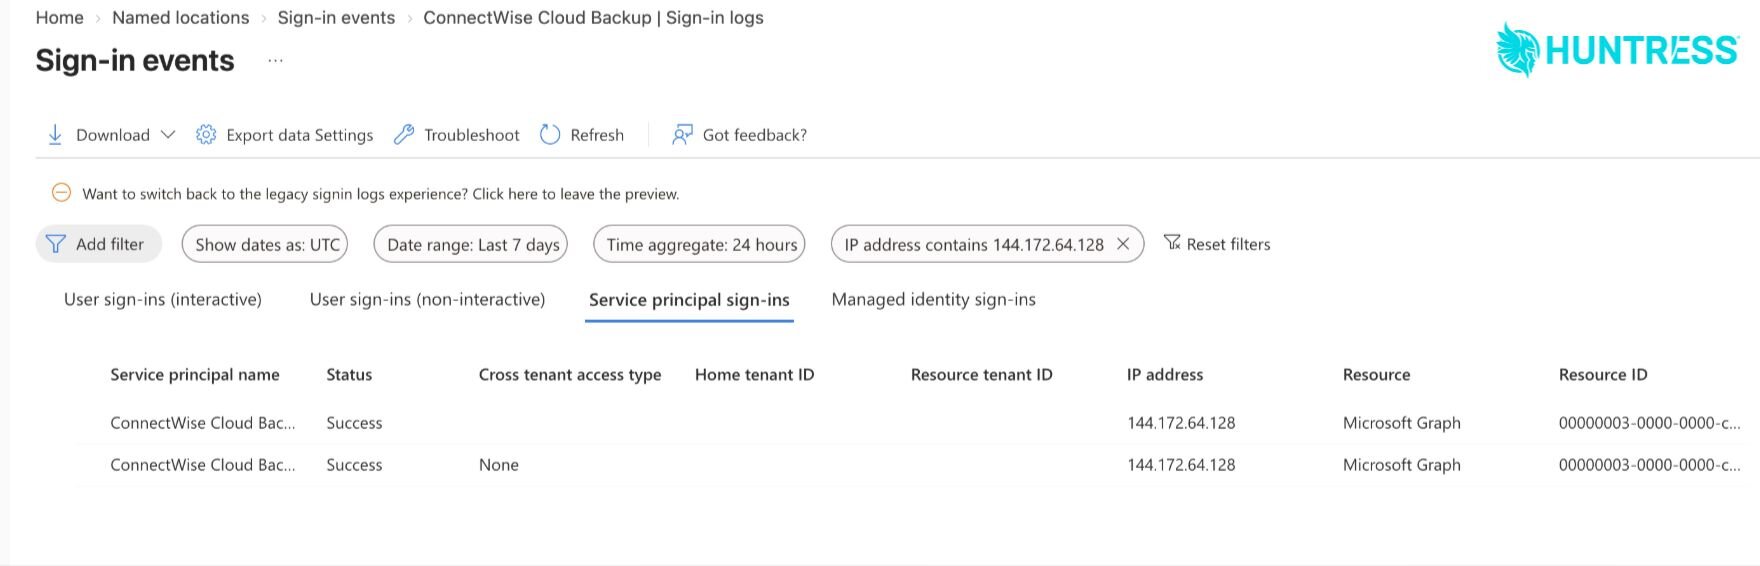
ConnectWise Cloud Backup Breach: What Happened, Who's Hit
A compromised vendor credential for ConnectWise's Cloud Backup app let an attacker sign into dozens of customers' Microsoft 365 tenants before ConnectWise shut the app down.
 Comparison
LastPass vs 1Password: Price, Security and Which to Choose
A factual, 2026 price-and-security comparison of LastPass and 1Password, including LastPass's own disclosures about its 2022 security incidents.
 News
French Supermarket Hack Heats Fridges to 50°C, Sparks Fires
A cyberattack on Danfoss refrigeration controllers pushed fridges to 50°C at hundreds of French supermarkets, spoiling food, sparking fires, and triggering ANSSI and prosecutor investigations.
 Explainer
What Is Smishing? SMS Phishing Scams, Explained
Smishing is phishing delivered by text message, using fake delivery, bank or prize texts to steal information. Here is how it works, how to spot it, and what to do.
 Explainer
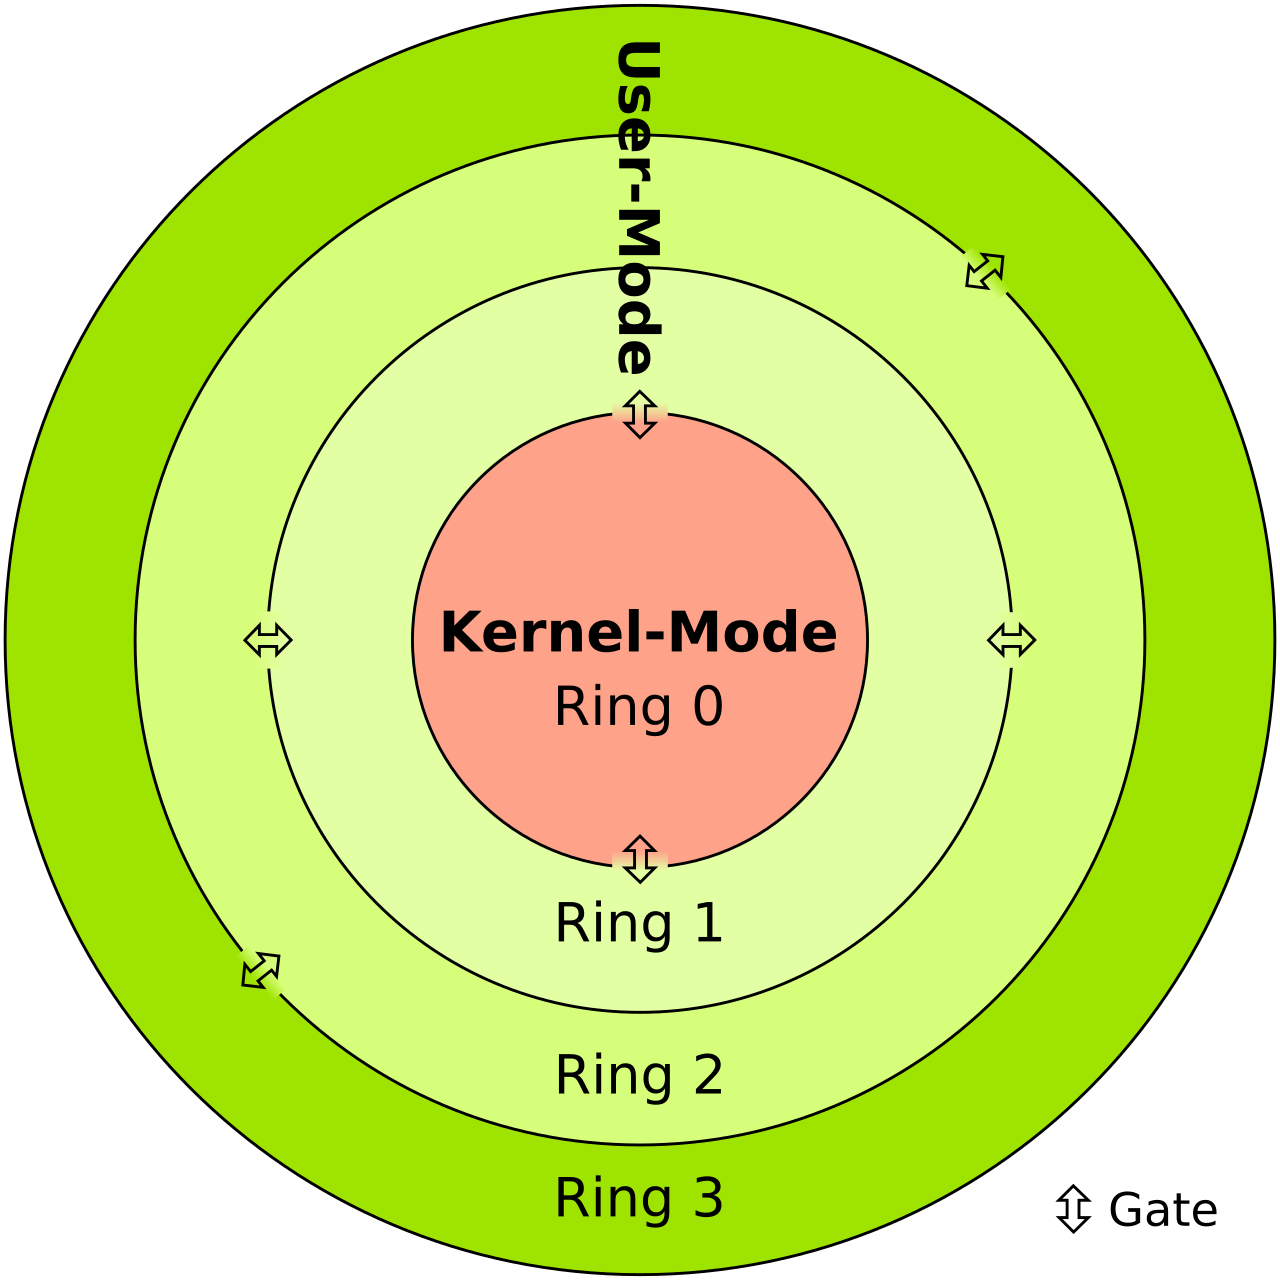
What Is a Rootkit? How It Works and How to Remove It
A rootkit is malware built to hide — from you and from your antivirus. Here's how these stealth infections work, the warning signs, and what actually gets rid of one.
 News
CVE-2026-104935: Ivanti Connect Secure Zero-Day Gives Root Access
A threat actor dubbed UTA0576 chained three Ivanti Connect Secure zero-days to gain unauthenticated root on fully patched VPN appliances, Volexity says.
 Comparison
Google Password Manager vs Apple Passwords: Which Should You Use?
Google and Apple both bundle a free password manager into their platforms now. Here is how passkey support, verification codes, and cross-platform reach compare.
iRhythm Data Breach: What Happened to Your Zio Monitor Data
Hackers stole patient data from the Zio heart monitor maker’s third-party business apps. Here’s what iRhythm has confirmed, what’s still unclear, and what to do now.
 Explainer
What Is Mark of the Web (MOTW)? How It Stops Malicious Files
Windows quietly tags every file you download from the internet. Here is how that Mark of the Web tag protects you, and how a new CVE just slipped past it.
 News
CVE-2026-96951: Windows Shell Flaw Exploited, Patch Now
Microsoft confirms active exploitation of a Windows Shell command-injection bug that bypasses Mark of the Web protections. CISA's patch deadline already passed.
 Comparison
VPN vs Tor: Which One Should You Use to Protect Your Privacy
A VPN encrypts traffic through one server you have to trust. Tor splits it across three volunteer relays so no one sees the whole picture. Here is the real difference.
 News
Ahold Delhaize Cyberattack: Food Lion, Stop & Shop Hit
Ahold Delhaize took systems offline after a cybersecurity incident disrupted online ordering at Food Lion, Stop & Shop, Hannaford, Giant Food and its European banners. Stores stayed open, and the company says it has no evidence yet that customer data was taken.
 Explainer
What Is Zero Trust Security? Principles and How It Works
Zero trust replaces implicit network trust with continuous verification of every user, device, and request. Here is how the model actually works.
NewsIvanti Connect Secure Zero-Day Puts CISA Deadline Today
Volexity caught attackers chaining three Ivanti Connect Secure zero-days for unauthenticated root access. CISA's patch deadline for CVE-2026-104935 is today.
 Comparison
Malwarebytes vs Norton 360: Which Antivirus Wins in 2026?
A head-to-head on pricing, real-time protection, AV-TEST and AV-Comparatives lab results, bundled VPN and extras, and system impact, so you can pick the right one.
 News
CISA KEV: Atlassian CVE-2026-21589 Exploited, Patch Deadline Oct. 18
CISA confirms active exploitation of the Atlassian file-access flaw CVE-2026-21589 and gives agencies just three days to patch or isolate affected servers.
 Explainer
What Is a Passkey and How Does It Work?
Passkeys swap passwords for cryptographic keys unlocked by your fingerprint, face, or PIN. Here's how they work, why they can't be phished, and how to turn one on.
 News
PAN-OS Vulnerability CVE-2026-0322: What It Is and How to Patch It
CISA added CVE-2026-0322, an authenticated RCE in PAN-OS's management interface, to its KEV catalog, setting a 3-day federal patch deadline.
 Comparison
Bark vs. Qustodio vs. Aura: Parental Control Apps Compared
Bark, Qustodio, and Aura's parental-control plans take different approaches to screen time, filtering, location, and AI chat monitoring. Here's how 2026 pricing compares.
 News
Patch Tuesday October 2026: Microsoft's Biggest Update Ever
Microsoft's largest Patch Tuesday on record patches over 1,400 flaws, including a Windows Shell zero-day CISA has ordered agencies to fix by October 16.
 Explainer
What Is a Deepfake Scam? How AI Voice and Video Fraud Works
AI voice cloning and video deepfakes are turning fake emergencies, CEO fraud, and romance cons into something far harder to spot. Here is how they work, and how to verify who you are talking to.
 News
CVE-2026-96940: Microsoft Exchange Vulnerability, Patch Now
Microsoft's out-of-band fix for CVE-2026-96940 patches a CVSS 8.8 Exchange Server flaw that let authenticated attackers read other users' mailboxes. Exchange Online is unaffected.
 Comparison
Windows Hello vs Face ID: Which Biometric Login Is Safer?
A side-by-side look at how Microsoft's Windows Hello and Apple's Face ID authenticate users, store biometric data, resist spoofing, and support FIDO2 passkeys.
NewsIvanti Connect Secure CVE-2026-104935: Patch Now, CISA Says
CISA confirms active exploitation of an authentication-bypass bug in Ivanti Connect Secure and gives federal agencies a three-day BOD 26-04 deadline to patch or disconnect.
 Explainer
What Is a Zero-Click Exploit? How It Works and How to Protect Yourself
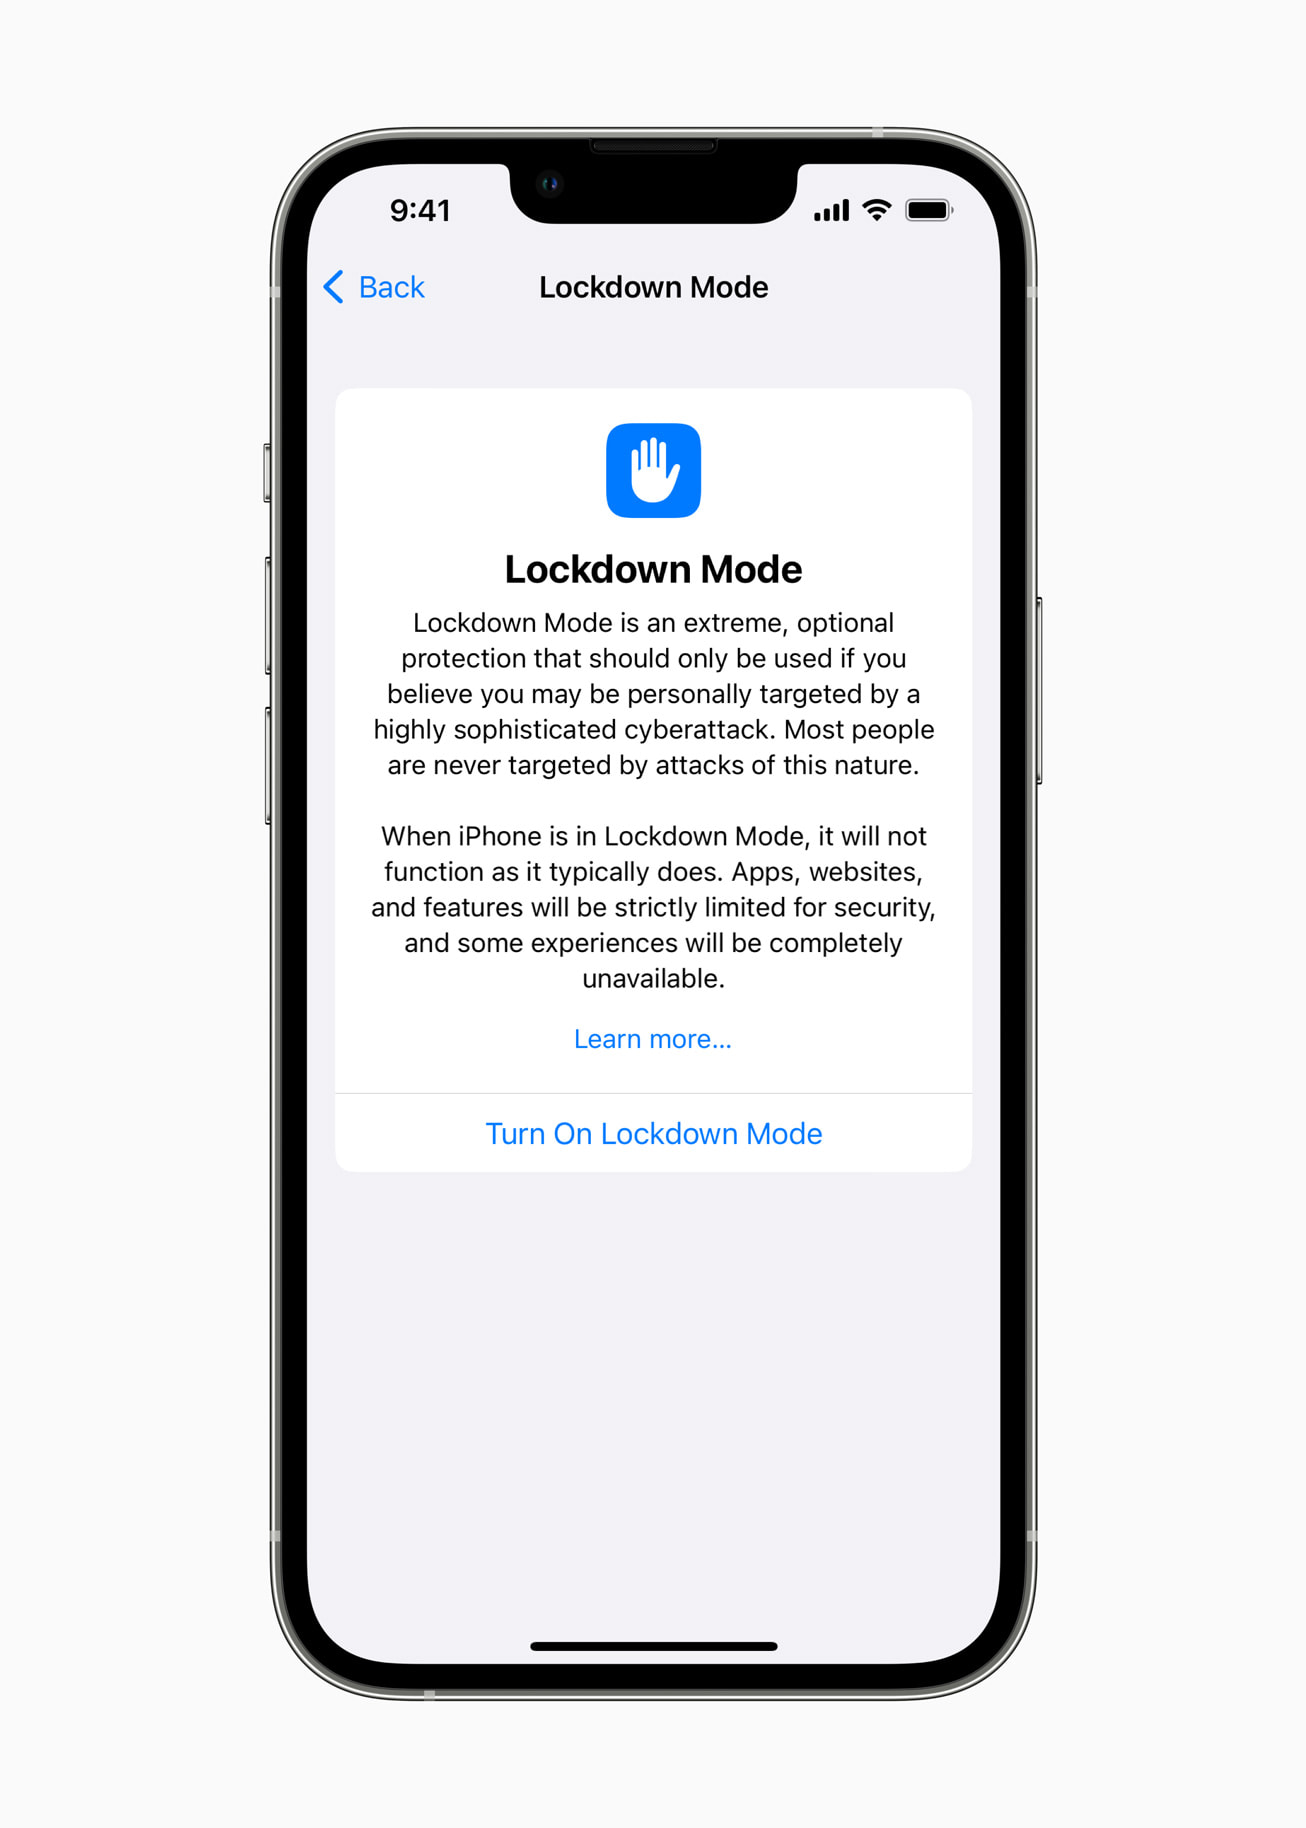
No link, no tap, no download needed. Here is how zero-click exploits like Pegasus and FORCEDENTRY work, and how Apple's Lockdown Mode helps.
NewsAhold Delhaize Data Breach: What Happened and Who's Affected
Ahold Delhaize, parent of Stop & Shop, Hannaford, Giant Food and Food Lion, took systems offline after a cybersecurity incident. Here's what it has confirmed.
 Comparison
Passkeys vs Passwords: Which Is More Secure?
A security comparison of passkeys and passwords: how each works, phishing and credential-stuffing resistance, recovery trade-offs, and where passkeys are supported today.
 Comparison
iCloud Private Relay vs VPN: What’s the Difference, and Which Do You Need?
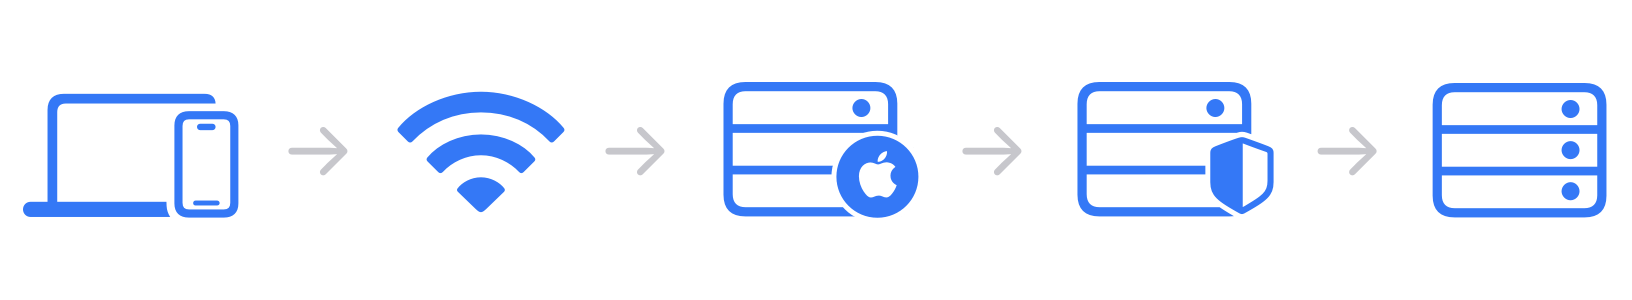
Apple's Safari-only privacy tool and a full VPN solve different problems. Here's exactly what Private Relay protects, what it misses, and when you still need a VPN.
 News
Trump Mobile Data Breach: What Happened and Who's Affected
A leak group calling itself BYOD says it exposed names, emails, phone numbers and home addresses tied to 3,615 Trump Mobile customers. Trump Mobile has not confirmed the breach.
ExplainerWhat Is Credential Stuffing? Meaning, Attack and Defenses
Credential stuffing uses stolen passwords from other breaches to break into your accounts. Here is how it works, how it differs from brute force, and how to stop it.
 News
SonicWall SMA1000 CVE-2026-102255: Max-Severity SSRF — Patch Now
A pre-auth SSRF bug with a perfect 10.0 CVSS score lets unauthenticated attackers abuse SMA1000 WorkPlace portals. SonicWall's Oct. 6 hotfixes close it — here's what to patch.
 Comparison
NordVPN vs ExpressVPN: Price, Speed and Streaming Compared
NordVPN and ExpressVPN compared on plans, speed, server networks, streaming, and logging policy, with a clear verdict on which VPN to pick.
 News
DriveWealth Data Breach: What Happened and Who's Affected
DriveWealth, the broker behind Revolut and Hatch US stock trading, confirmed names and other personal data were stolen in a September 2026 network breach.
ExplainerWhat Is Malware? Types, Warning Signs and How to Remove It
A plain-language guide to malware: what it is, the main types like viruses and trojans, how infections happen, warning signs, and how to remove and prevent it.
 News
Georgia Power Data Breach: What Happened and Who's Affected
A breach of Georgia Power's online customer portal, part of a wider Southern Company incident, exposed contact details and partial Social Security numbers for roughly 300,000 Georgia customers.
 Comparison
Google Authenticator vs Microsoft Authenticator vs Authy: Compared
All three major authenticator apps are free, but they back up, sync across devices, and handle push approval differently enough to change which one you should install.
 News
ASOS Data Breach: What Happened and Who's Affected
A hijacked push notification system, a Telegram threat, and an NCSC warning to every ASOS customer: here's what's confirmed so far and what to do now.
 Explainer
What Is Social Engineering? How It Works and How to Stay Safe
What social engineering is, why urgency and trust make it work, and how to stop it from becoming a bigger breach.
 News
LibreOffice Fixes Critical RCE Bug and 5 Other Flaws — Patch Now
The Document Foundation patched six LibreOffice vulnerabilities, including a remote-code-execution flaw triggered by simply opening a document; update to 26.2.5 or 26.8.0 now.
 Comparison
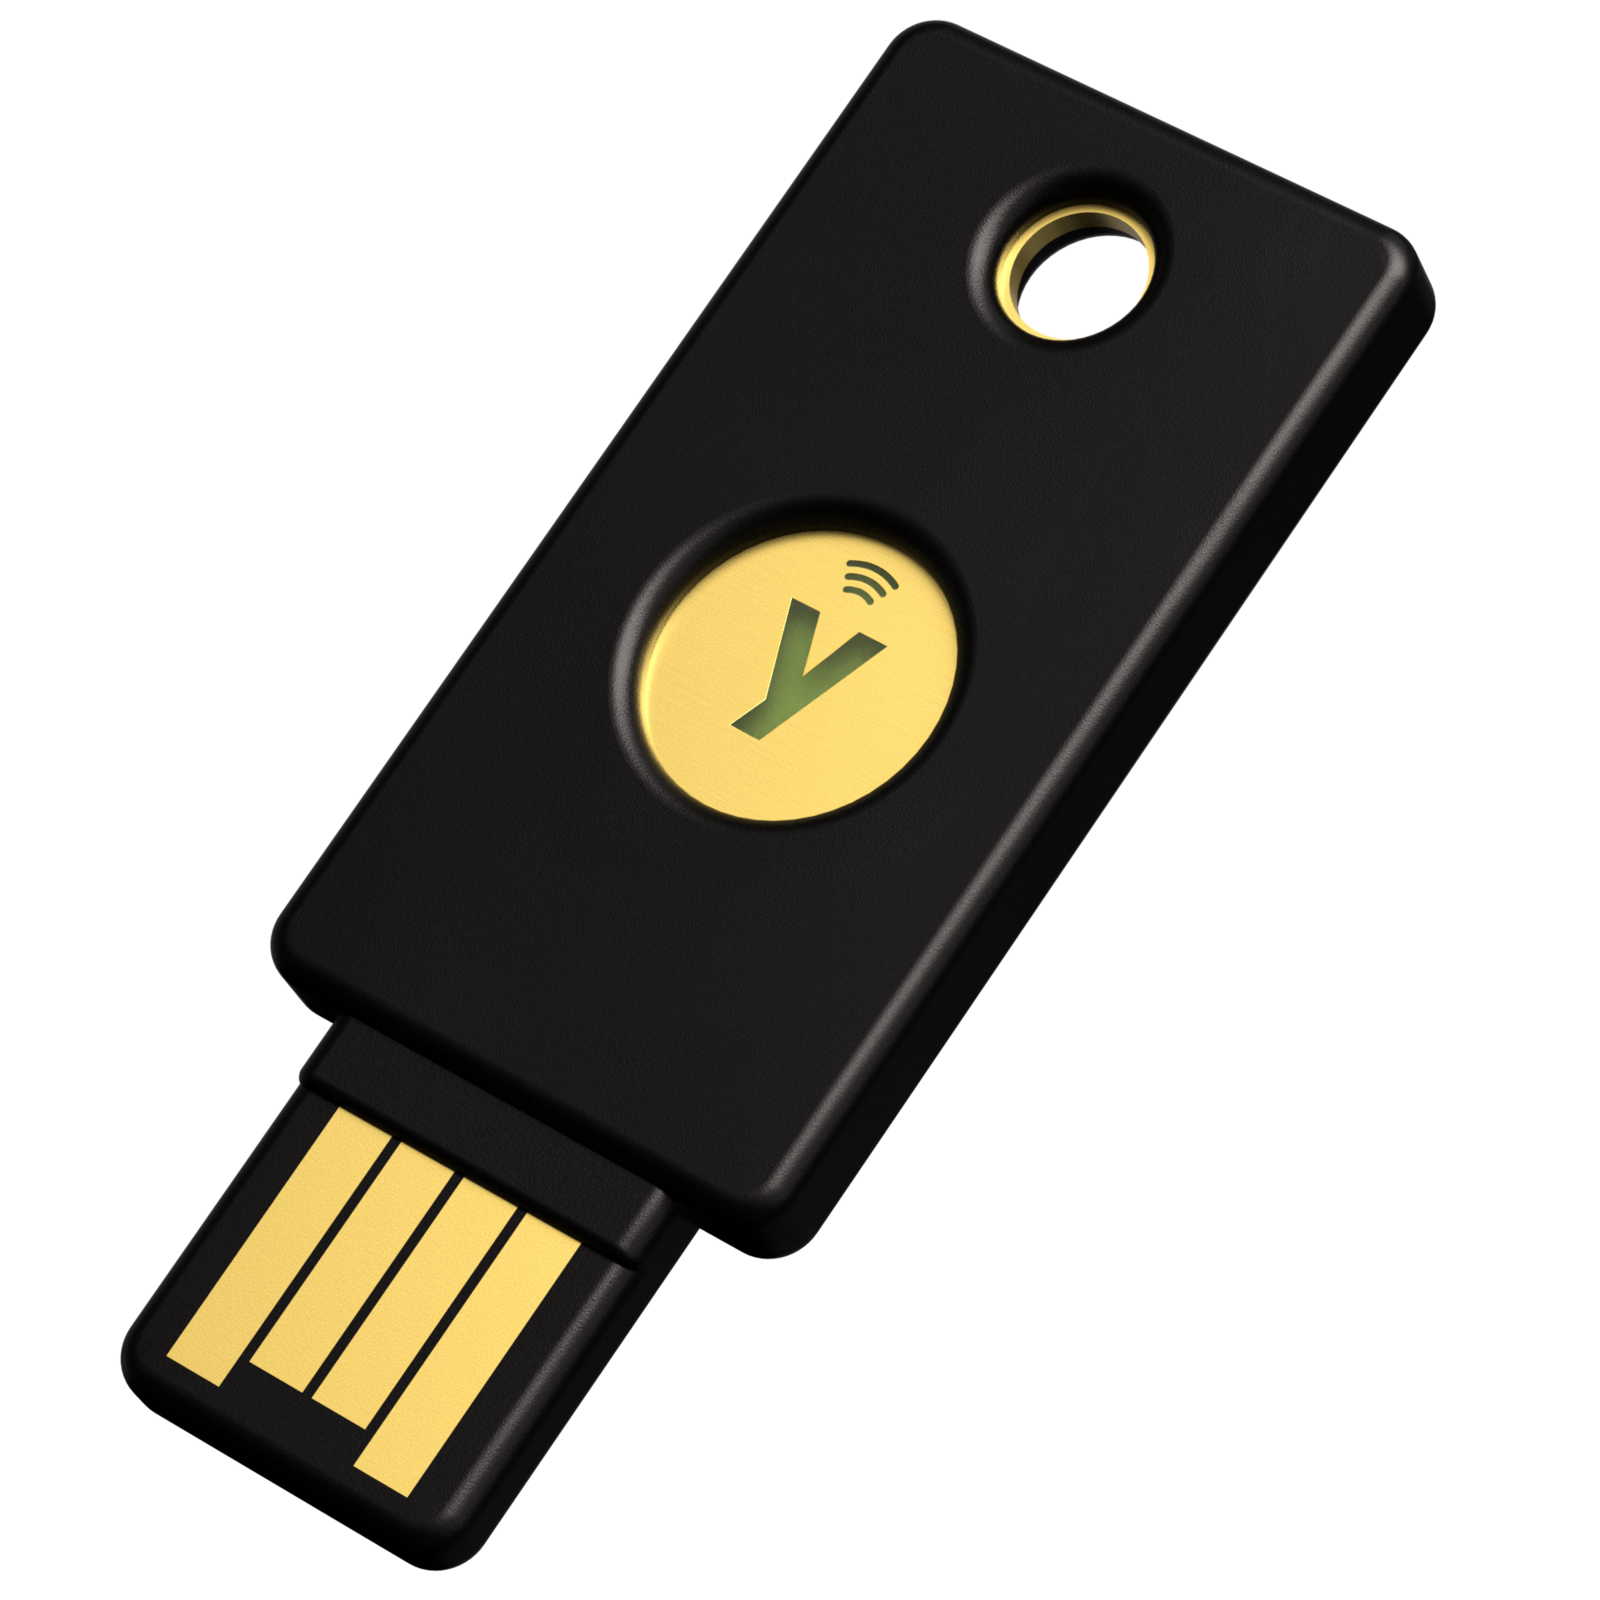
YubiKey vs Google Titan Security Key: Price, Features and Which to Buy
Google's Titan Security Key costs less and covers passkeys and U2F. Yubico's YubiKey 5 Series costs more but adds PIV, OpenPGP, SSH and OTP. Here's which one fits your accounts.
 News
Zammad Zero-Days (CVE-2026-102489, CVE-2026-102490): Patch Now
CISA added both Zammad zero-days to its KEV catalog after DIVD says an AI agent chained them to hijack a session, run code, and gain root inside its own network.
 Explainer
What Is a Password Manager? How It Works and Do You Need One
What a password manager actually does, how its zero-knowledge encryption protects your vault, autofill and passkey support, and whether you need one.
 News
Atlassian CVE-2026-21589: Critical File-Read Flaw, Patch Now
A critical, unauthenticated file-read bug hits eight self-hosted Atlassian products. Cloud is already patched; no exploitation confirmed yet, but patch now.
 Comparison
Ring vs Arlo vs Google Nest: Price, Features and Which to Buy
Arlo's $29.99 unlimited-camera plan leads on AI detection, Ring is cheapest for whole-home video history, and Google Nest wins for Gemini-connected smart homes.
 News
FortiMail CVE-2026-104286: Critical Zero-Day Exploited, Patch Now
A critical, unauthenticated path-traversal flaw in FortiMail is under active attack. CISA added it to its exploited-vulnerabilities list the same day Fortinet disclosed it.
 Explainer
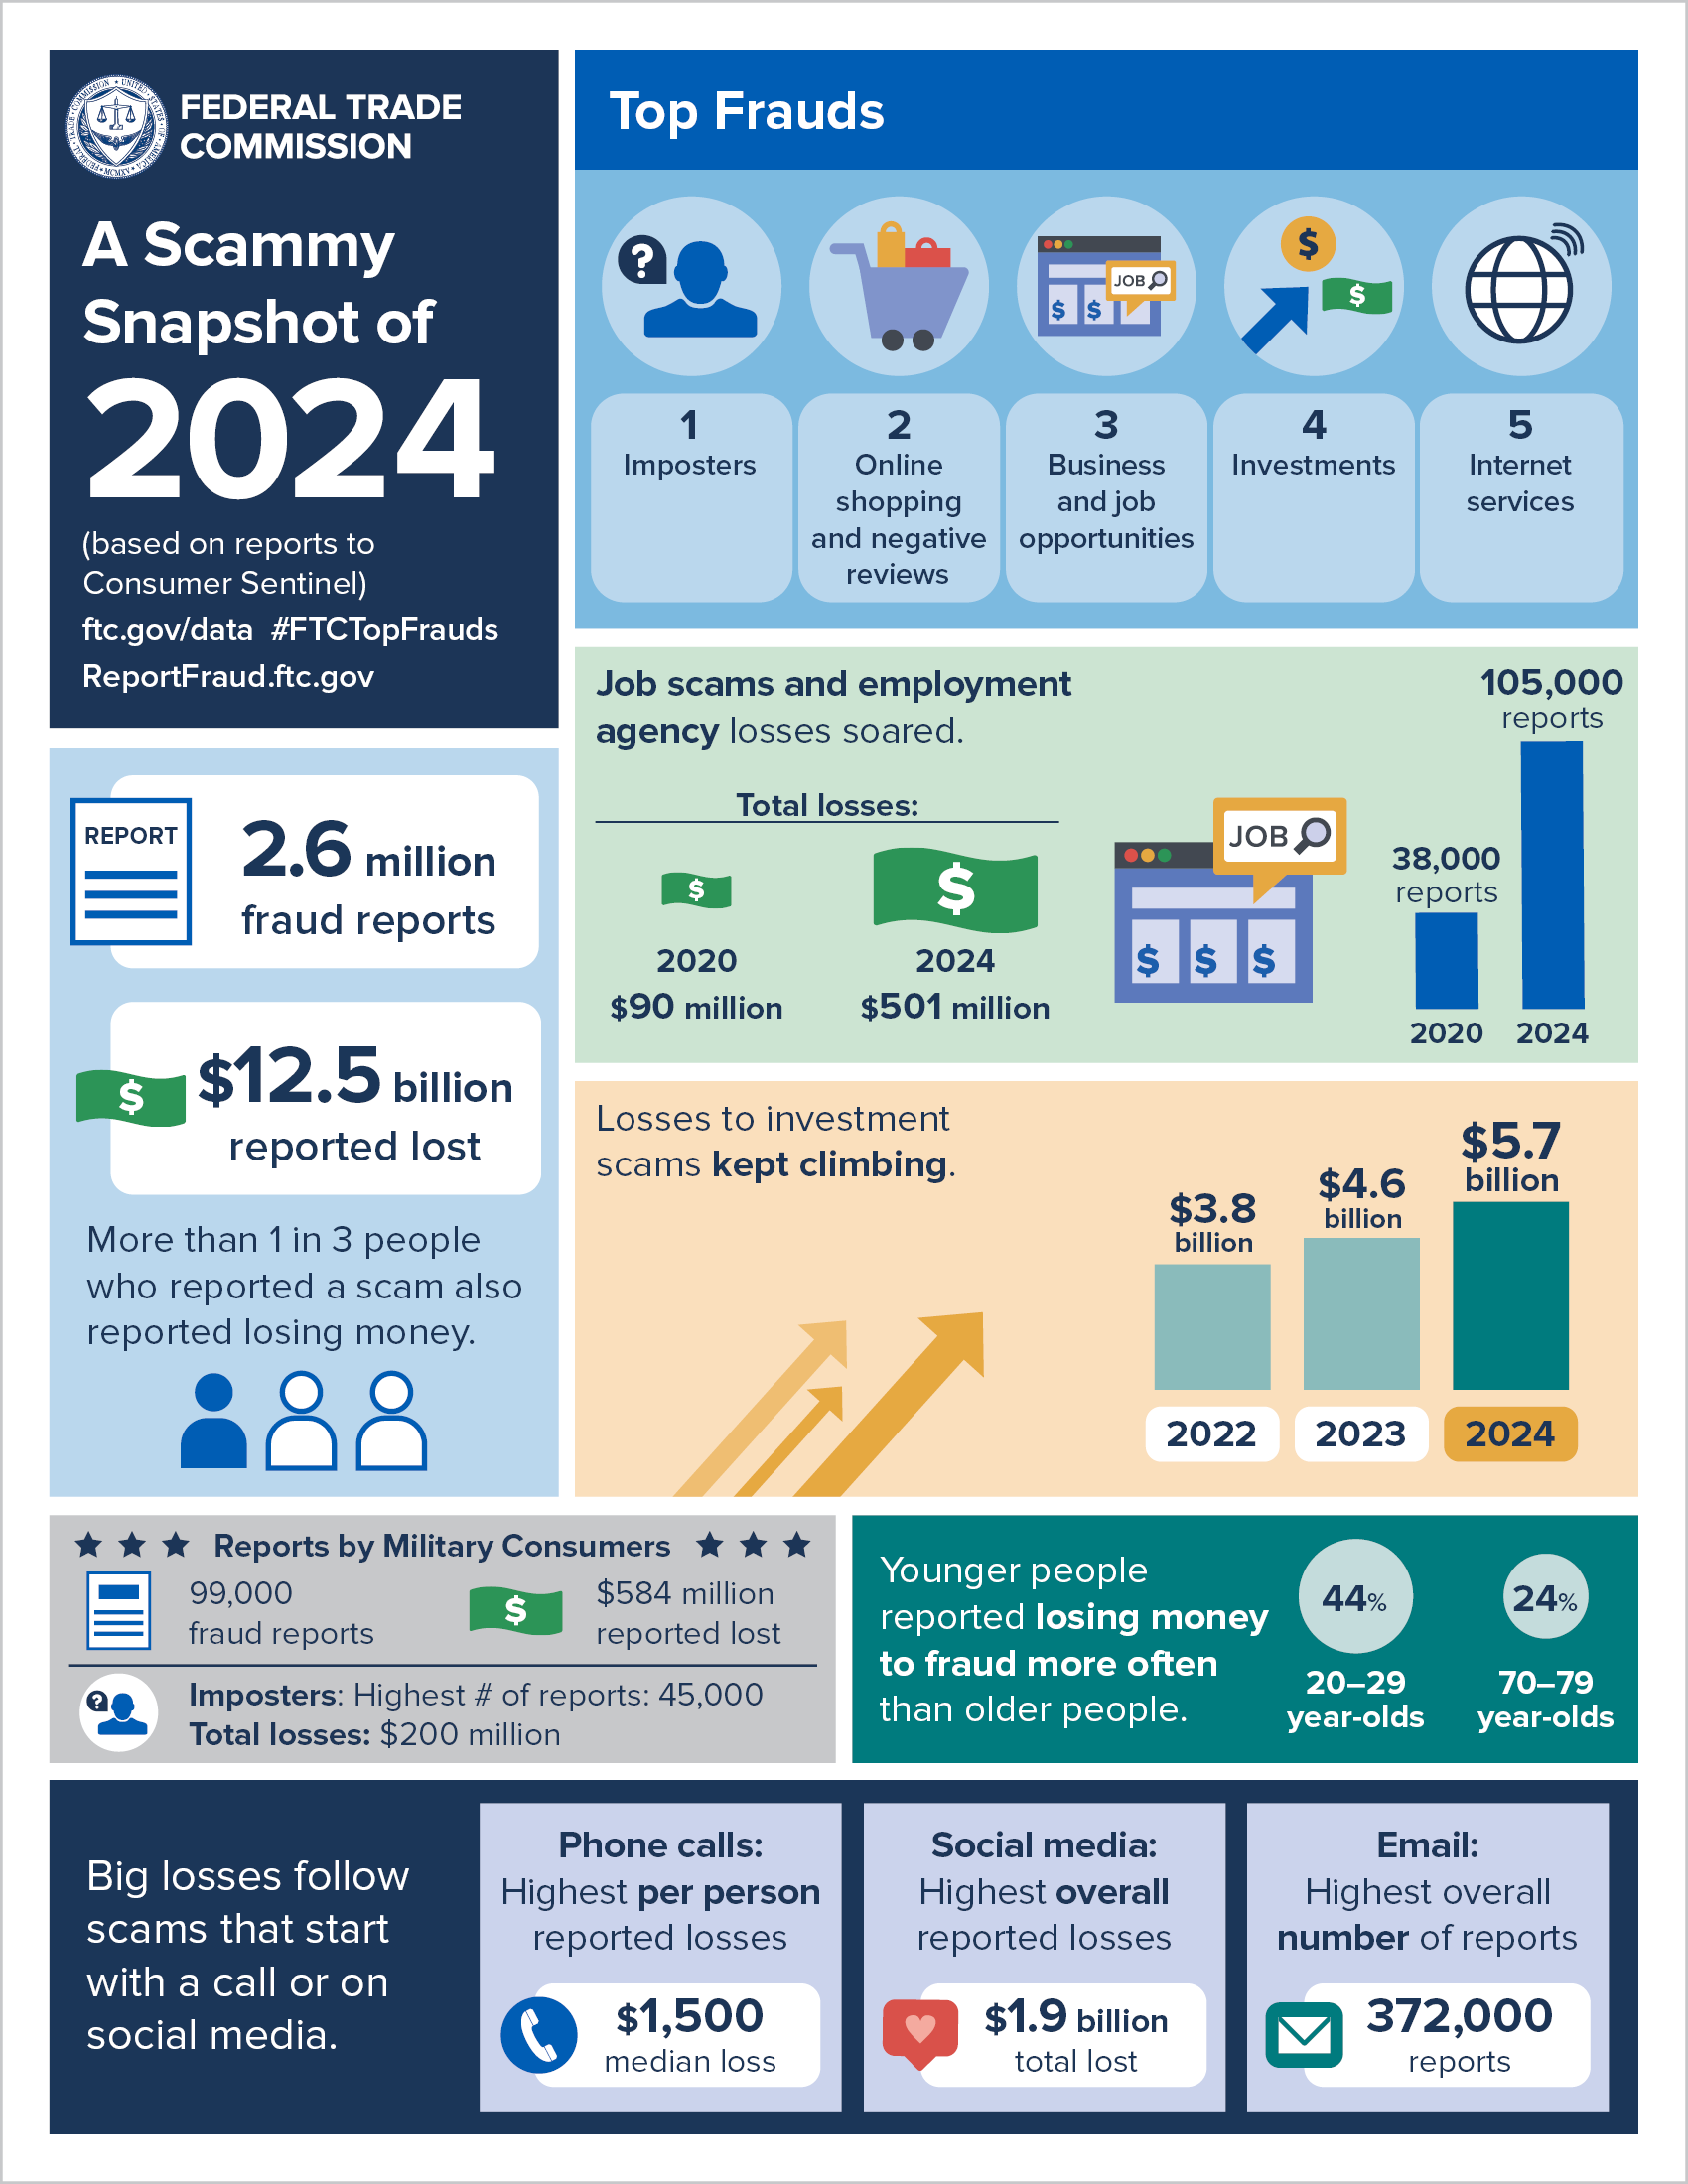
What Is a Pig Butchering Scam? How It Works, Explained
A fake online relationship paired with a fake crypto investment, explained step by step using FBI, FTC, and Treasury data, plus red flags and where to report it.
 News
Arizona Supreme Court Data Breach: What Happened and Who's Affected
A phishing click exposed Social Security numbers, protective-order files and 150,000+ foster-care records in Arizona's court system. Here's what's known and how to protect yourself.
 Comparison
DeleteMe vs Incogni vs Aura: Price and Features Compared
DeleteMe, Incogni, and Aura all scrub your data from broker sites, but pricing, coverage, and who does the removal differ sharply. Here is the breakdown.
 News
Citrix NetScaler CVE-2026-88779: New SAML Zero-Day, Patch Now
A new NetScaler memory-buffer bug tied to SAML authentication is under active exploitation. Citrix patched it in CTX697174; CISA set an October 7 KEV deadline.
 Explainer
What Is a VPN? How It Works and Whether You Need One
A plain-language guide to what a VPN actually does, how the encrypted tunnel works, and when you do (and don't) need one.
 News
Frontline Education Data Breach: What Happened, Who's Affected
A vulnerability in third-party software let attackers into Frontline Education's systems, exposing school-district employee data. Here's what's known and what to do next.
 Comparison
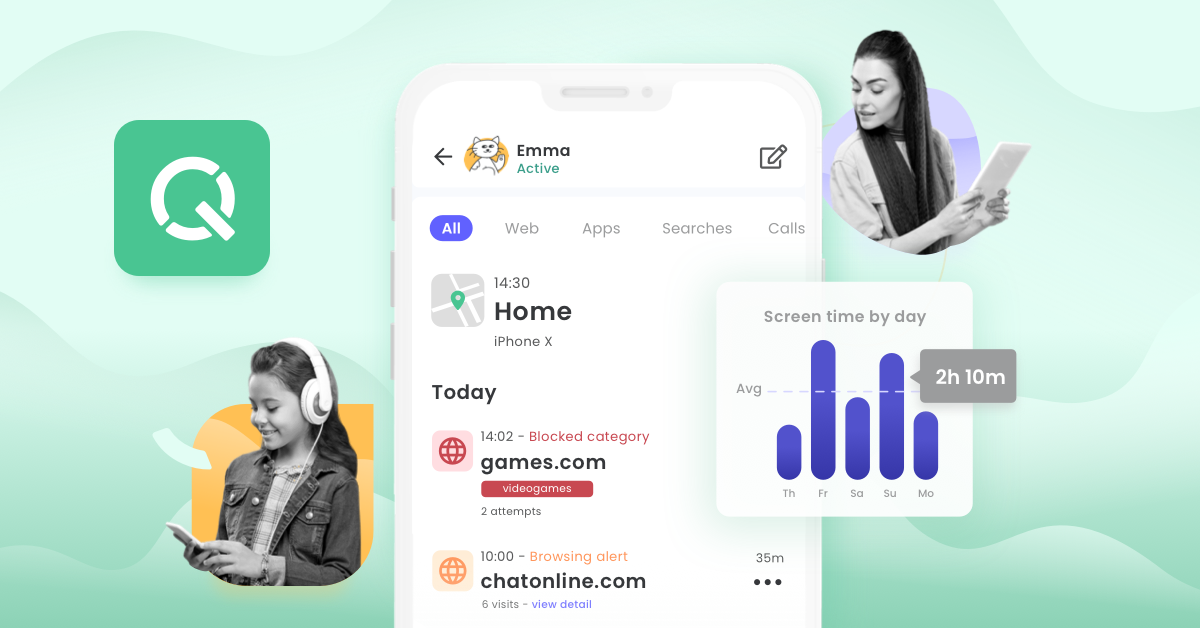
Bark vs Qustodio vs Net Nanny: Price and Features Compared
Bark, Qustodio, and Net Nanny take different approaches to screen time, filtering, and monitoring. Here is what each actually costs and covers.
 News
Windows Netlogon RCE (CVE-2026-41089): Is It Exploited? Patch Now
A 9.8 CVSS Netlogon RCE in Windows Server domain controllers, patched in May 2026 — now caught in a dispute between Belgium's CCB and Microsoft over active exploitation.
 Guide
QR Code Scams Explained: How to Spot and Avoid Quishing
Scammers hide malicious links inside QR codes on parking meters, packages, and texts. Here is how quishing works, the warning signs, and what to do if you scan a bad one.
 News
Pentagon Data Breach: What Happened to the DMDC and Who Was Affected
Over 3 million people had personal data exposed when a Pentagon personnel system went unprotected for months. Here is what is confirmed and what is still only reported.
Comparison1Password vs Dashlane: Price, Features and Security Compared
1Password's $2.99-a-month Individual plan undercuts Dashlane's $5.42 Premium tier, but Dashlane bundles a VPN and scam alerts. Here is the full price and security breakdown.
 News
Zammad Zero-Day Chain Exploited by AI Agent: Patch Now
An unauthenticated session-fixation RCE and a local root escalation in Zammad combine into full root takeover. CISA's KEV deadline is October 5, 2026.
 Explainer
What Is a Zero-Day Vulnerability? How It Works and How to Stay Safe
What a zero-day vulnerability, exploit, and attack actually mean, how the CVE disclosure-to-patch cycle works, and the concrete steps that reduce your risk.
NewsAdobe Commerce CVE-2026-71362: Critical Flaw Exploited, Patch Now
A critical incorrect-authorization bug in Adobe Commerce and Magento Open Source is being actively exploited to hijack customer sessions. CISA set a September 27 federal patch deadline.
 Comparison
CrowdStrike vs SentinelOne: EDR Price and Features Compared
A buyer-focused comparison of CrowdStrike Falcon and SentinelOne Singularity: published pricing, detection approach, platform coverage and which fits your org size.
NewsFortiMail CVE-2026-104286: Critical Flaw Exploited, Patch Now
CISA confirms active exploitation of a critical, unauthenticated FortiMail path traversal flaw and gives federal agencies until October 4 to patch or mitigate.
 Explainer
Ransomware Explained: What It Is and How to Stay Safe
What ransomware is, how attacks unfold, whether paying the ransom ever makes sense, and the steps that actually reduce your risk.
 News
Kiteworks Patches Dozens of Critical Flaws After Shutdown Scare
Days after warning customers to shut systems down over a federal threat tip, Kiteworks disclosed dozens of new vulnerabilities, including a critical flaw letting attackers hijack admin accounts.
ComparisonSignal vs WhatsApp vs Telegram: Which Is Most Private?
Encryption, metadata, ownership and backups compared head-to-head to find out which of the three messaging apps actually protects your privacy.
NewsCisco Catalyst SD-WAN Manager CVE-2026-76504: Patch Now
CISA confirms active exploitation of a critical, unauthenticated Cisco Catalyst SD-WAN Manager auth-bypass flaw and gives federal agencies until October 3 to patch.
 Guide
SIM Swap Scams Explained: Warning Signs and How to Protect Yourself
Criminals can hijack your phone number to intercept SMS codes and raid your accounts. Here is how SIM swapping works, the warning signs, and how to lock your number down.
 News
MikroTik Routers Under Active Attack: Patch RouterOS Now
CERT Polska and CISA say attackers are chaining RouterOS flaws to seize control of internet-exposed MikroTik routers without any login credentials.
 Comparison
Windows Defender vs Norton vs McAfee: Do You Need Paid Antivirus?
Microsoft's built-in antivirus scores well in independent testing, but Norton 360 and McAfee bundle a VPN, dark web monitoring and identity protection it lacks. Here's what actually differs.
NewsWordPress CVE-2026-87902: Critical RCE Flaw Exploited, Patch Now
WordPress 7.1.2 fixes a critical, unauthenticated path-traversal bug in get_page_template() that attackers began exploiting within hours of disclosure. CISA has ordered federal agencies to patch fast.
 Explainer
Phishing Emails Explained: How to Spot Them and What to Do
How to spot a phishing email by its real red flags, the scams impersonating Amazon and Geek Squad right now, and what to do if you clicked or handed over a password.
 News
Apple CVE-2026-86950 Zero-Day Exploited: Update iOS, macOS Now
A Core Graphics flaw fixed in iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1 was used in a targeted attack. Here's what Apple says and what to do.
 Comparison
LifeLock vs Aura vs Identity Guard: Prices and Features Compared
LifeLock, Aura, and Identity Guard all monitor your identity and credit, but pricing tiers, insurance limits, and family coverage differ sharply. Here's how their official plans compare.
Cisco ISE, Email Gateway Zero-Days Exploited: Patch Now
Two Cisco zero-days—an ISE authentication bypass and a Secure Email Gateway SQL injection—are under active exploitation and listed in CISA's KEV catalog.
 Guide
How to Opt Out of Data Brokers and People-Search Sites
Data brokers compile and sell your personal details to anyone who pays. Here's how they get your data, why it matters, and how to opt out for free.
NewsCitrix NetScaler CVE-2026-88771 & 88772 Exploited: Patch Now
Two critical NetScaler ADC and Gateway zero-days are being exploited in the wild. Here is what Citrix's CTX697096 bulletin and CISA's KEV listing say, and how to patch.
 Comparison
Norton vs Bitdefender vs McAfee: Prices and Features Compared
A side-by-side look at Norton 360, Bitdefender Total Security, and McAfee Total Protection — pricing, renewal traps, device coverage, and the security extras each one bundles in.
 News
September 2026 Patch Tuesday: Two Windows Zero-Days Under Attack
CISA added two actively exploited Windows privilege-escalation flaws to its KEV catalog the same day Microsoft patched them in September's Patch Tuesday release.
ExplainerWhat Is Have I Been Pwned? How to Check If You've Been Hacked
Have I Been Pwned is a free, legitimate breach-notification service run by security researcher Troy Hunt for checking your email and passwords.
 News
CVE-2026-65660: SharePoint Flaw Under Active Attack, Patch Now
CVE-2026-65660 lets authenticated attackers hijack on-premises SharePoint Server via a ToolPane code-injection bug. CISA confirms active exploitation and sets a September 28 deadline.
 Guide
How to Set Up an Authenticator App for Two-Factor Authentication
Text-message codes can be stolen with a SIM swap. Here is how to switch your accounts to an authenticator app, step by step, and avoid getting locked out.
ComparisonExpressVPN vs Surfshark vs Proton VPN: Prices and Features Compared
Surfshark is cheapest upfront, Proton VPN undercuts Surfshark month to month and ExpressVPN renews highest. Every tier compared from the official pricing pages.
 News
IDScan.net Data Breach: Was Your Driver’s License Exposed?
The ID-scanning firm behind countless counter checks says names and license numbers were taken. A seller claimed 153 million records. Here is what to do.
 News
Chrome 154 Security Update: 108 Fixes, 11 Critical and How to Update
Chrome 154 fixes 108 security bugs, 11 of them rated Critical. Here is what the Critical fixes cover and how to make sure you are on the patched version.
GuideHow to Set Up Passkeys on iPhone, Android and Windows
Replace passwords with your face, fingerprint or PIN. Step-by-step passkey setup for iPhone, Android, Windows, Google and Microsoft accounts, straight from each company’s own instructions.
 Comparison
Bitwarden vs 1Password vs Proton Pass: Prices and Features Compared
Official prices, free plans, family plans and security features side by side, so you can pick the password manager that fits your budget and how you share logins.
 News
F5 BIG-IP APM CVE-2026-94127 Exploited: Hotfixes and Mitigation
F5 says a critical heap overflow in BIG-IP APM’s OAuth authorization server is under attack. Here is who is exposed, which hotfix to install and what to look for in logs.
 News
Check Point CVE-2026-93616 and CVE-2026-85102 Exploited: Patch Now
A management-server zero-day used since July and a VPN bug now hitting Spark firewalls: here are the fixed Jumbo Hotfix takes, the log checks and the September 25 CISA deadline.