Pentagon Data Breach: What Happened to the DMDC and Who Was Affected
Over 3 million people had personal data exposed when a Pentagon personnel system went unprotected for months. Here is what is confirmed and what is still only reported.
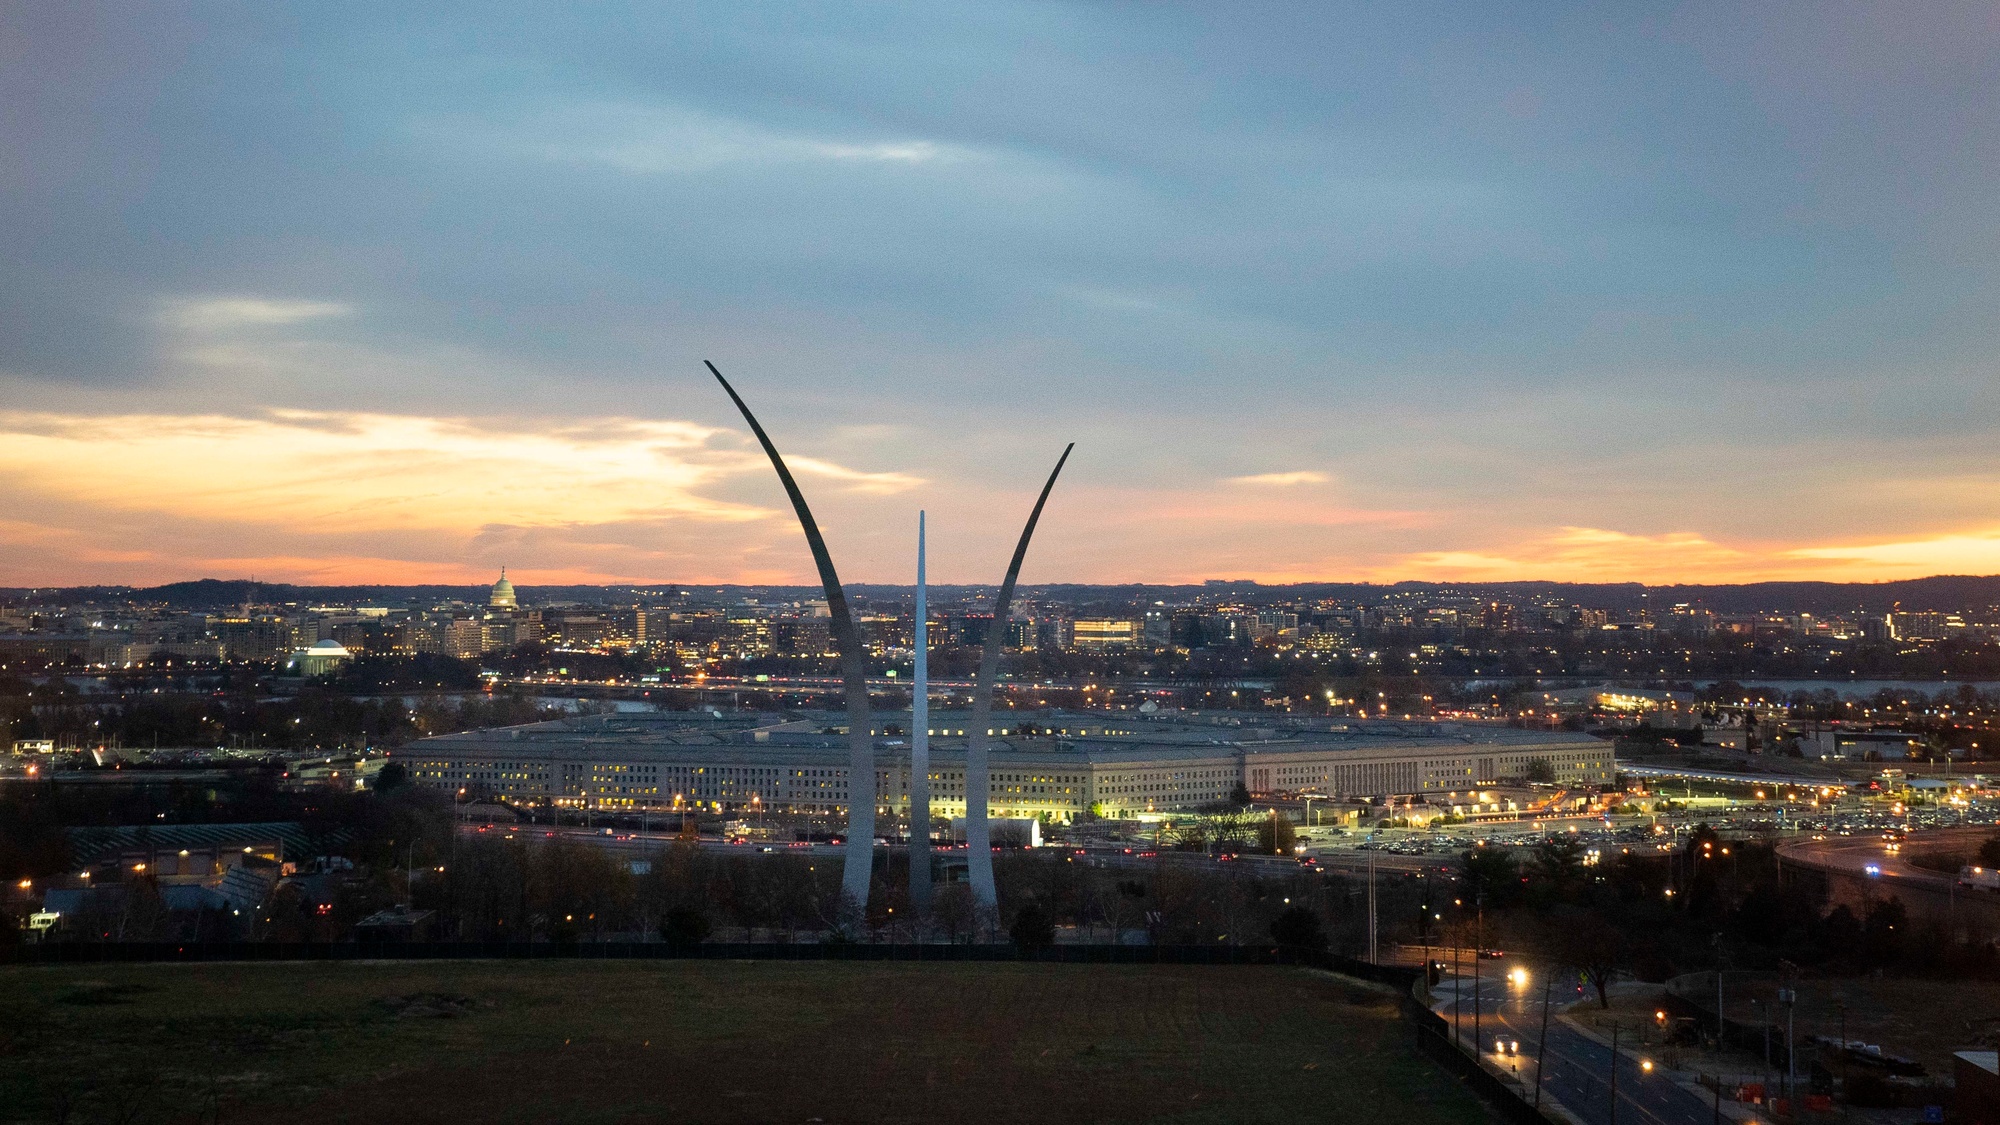
The Pentagon's Defense Manpower Data Center (DMDC) left an unencrypted file-sharing system exposed to unauthorized users for roughly nine months, from October 2025 until the vulnerability was discovered and patched on July 16, 2026. According to a Department of Defense notification letter dated September 18, 2026, the exposed files contained personal data — including Social Security numbers — belonging to more than 3 million people: about 2.8 million living current and former service members, civilian employees and their dependents, plus roughly 294,000 deceased former defense personnel or their dependents. Importantly, the Pentagon has not published a public press release confirming the incident. What is publicly known comes from that notification letter, whose authenticity two defense officials confirmed to reporters, and from consistent follow-up reporting by multiple independent outlets.
- Agency: Defense Manpower Data Center (DMDC), a personnel-records organization under the Office of the Secretary of Defense
- What was breached: An unencrypted internal file-sharing system
- Unauthorized access window: October 2025 to July 16, 2026
- Discovery date: July 16, 2026
- Notification letters dated: September 18, 2026
- Public reporting began: around September 24, 2026; widely corroborated by September 29, 2026
- People affected: 3,000,000+ (about 2.8 million living, about 294,000 deceased)
- Data exposed: Social Security numbers plus at least one of: name, date of birth, contact details, sex, race, military job/occupational-specialty information
- Remediation: File-sharing system patched; one year of credit monitoring and identity-restoration services offered through IDX
- Evidence of misuse: None reported as of this writing, per the notification letter
What happened at the DMDC
DMDC is the Pentagon's central personnel-records clearinghouse. It has operated since 1974 under the Office of the Secretary of Defense and maintains records that stretch back decades across every branch of the armed forces, the National Guard and Reserve, DoD civilian employees, and millions of their dependents. It is the system behind everyday military life — ID cards, DS Logon credentials, TRICARE eligibility checks, retirement and survivor records — which is exactly why a breach there is so consequential: the data isn't a single app's sign-up list, it's the backbone personnel file the rest of the defense bureaucracy relies on. Background on the agency's history and mission is documented on its Wikipedia entry.
Per the notification letter, a "small number of unauthorized users" gained access to a server holding unencrypted files containing personally identifiable information. The access point was a file-sharing system with a security vulnerability that, as far as has been disclosed, did not require any sophisticated exploit chain — it reportedly came down to sensitive files sitting unencrypted on a system that should not have been reachable by unauthorized users. DMDC says it immediately began privacy and cybersecurity incident-response procedures once the vulnerability was discovered, in line with Office of Management and Budget and internal Department guidance.
Timeline: from first access to public confirmation
The gap between when unauthorized access began and when the public learned about it was substantial — nearly a full year from first access to the first news reports, and more than two months from discovery to notification letters going out.
| Date | Event |
|---|---|
| October 2025 | Unauthorized users reportedly begin accessing the unencrypted DMDC file-sharing system |
| July 16, 2026 | DMDC discovers the security vulnerability and patches the file-sharing system |
| September 18, 2026 | Notification letters to affected individuals are dated |
| September 24, 2026 | Military Times reports on the breach after obtaining and verifying a copy of the letter; DoD does not immediately comment on scope |
| September 29–30, 2026 | Additional outlets (Security Affairs, cybernews.com, privacyguides.org and others) publish corroborating reports citing the same letter |
| October 3, 2026 | No DoD/defense.gov press release on the incident has been published as of this writing |
How many people were affected
The figure cited consistently across the notification letter and subsequent reporting is just over 3 million individuals, split roughly as follows: about 2.8 million living people (current service members, veterans, civilian DoD employees, and their family members with records in DMDC systems) and about 294,000 deceased former defense personnel or their dependents, whose records remained in the exposed system. DMDC's underlying databases are known to hold personnel records on tens of millions of people going back decades, so the roughly 3 million figure represents the subset whose files sat in the specific unencrypted file-sharing location that was accessed — not DMDC's entire archive.
Neither the letter nor subsequent press reporting has published a granular breakdown by military branch, active-duty versus veteran status, or geographic distribution. That level of detail, if it exists, has not been made public.
What data was exposed
The notification letter describes the exposure as a Social Security number combined with at least one additional identifier. Reporting based on the letter lists the following categories as having been exposed in unencrypted form:
| Reportedly exposed | Not reported as exposed |
|---|---|
| Social Security numbers | Financial account or payment card numbers |
| Full names | Login credentials or passwords |
| Dates of birth | Medical/health treatment records (beyond what overlaps with personnel data) |
| Contact information (address/phone) | Classified or operational military information |
| Sex and race | |
| Military job/occupational specialty details |
The combination of an SSN with a name, birth date and military occupational specialty is what makes this exposure particularly sensitive: it's enough to support identity theft and synthetic-identity fraud, and the occupational-specialty detail has also drawn attention from security researchers concerned about what it could reveal in aggregate about defense-related roles, even though no classified material has been reported as part of the exposure.
What the Pentagon has confirmed versus what has been reported
This distinction matters, especially for a story involving sensitive data on millions of current and former military personnel. Here is what can and cannot be verified directly against a DoD-owned source as of this writing:
- No public DoD/defense.gov statement. A search of defense.gov and DMDC's own pages turned up no press release, fact sheet or public statement from the Department of Defense specifically confirming this breach, its timeline or the number of people affected. The Department's public affairs apparatus has not, to date, issued the kind of on-the-record statement it typically provides for major incidents.
- The core account traces to one document: a notification letter. The timeline (October 2025 access, July 16, 2026 discovery), the data categories, and the September 18, 2026 letter date all originate from a breach-notification letter DMDC sent to affected individuals — the same kind of letter agencies and companies are required to send under breach-notification rules, not a press release intended for the public.
- That letter reached the public via Reddit, not DoD. A copy of the letter was posted to the r/AirForce community by someone who had apparently received it. It did not originate from a DoD-issued public statement.
- Two defense officials confirmed its authenticity to a reporter — on background. According to Military Times' September 24, 2026 report, two defense officials confirmed the leaked letter was genuine. That is a real, if limited, form of government confirmation — but it is anonymous-official confirmation of a document's authenticity, not an on-the-record DoD statement answering questions about scope, cause or total numbers.
- When asked directly for additional detail, DoD did not immediately respond. Military Times reported that the Department of Defense and DMDC did not immediately answer questions about exactly how many people were affected or who was behind the unauthorized access.
- The ~3 million/2.8 million/294,000 figures come from the letter as relayed by press, not from an independent DoD tally made public separately. Multiple outlets report the same figures, which is reassuring in that it suggests they are reading the same source document consistently — but it is still one underlying source, not several independent official disclosures.
In short: this is a real breach, acknowledged by the Pentagon's own personnel-records agency in writing to affected individuals, and consistently reported by multiple independent outlets. But the honest framing is "DoD-authored notification letter, confirmed authentic by anonymous officials and covered extensively by the press" — not "DoD public statement to the press." Readers should weigh the numbers accordingly: credible and consistent, but not yet independently verified through an on-the-record government disclosure.
How DMDC responded
Per the notification letter, DMDC says it "immediately initiated privacy and cybersecurity incident response actions in accordance with Office of Management and Budget and Department guidelines and policies" once the vulnerability was discovered on July 16, 2026. In practice, reporting indicates that meant patching the vulnerable file-sharing system and restoring it to normal operation. Federal agencies handling a PII breach are expected to follow the framework laid out in OMB Memorandum M-17-12, which governs how agencies assess risk of harm and decide on notification and remediation steps after a breach of personal information — the same guidance the letter references.
Officials have said, per the letter and subsequent reporting, that there is no evidence so far that the exposed data has been misused. That statement should be read for what it is: an assessment at the time of writing, not a guarantee, since SSN-based identity theft can surface months or years after a breach.
Credit monitoring and identity protection offered
Affected individuals who received the notification letter were offered one year of credit monitoring and identity-restoration services through IDX, a private identity-protection contractor commonly used by federal agencies and corporations for breach response. As with most breach-response credit monitoring offers, enrollment is opt-in and the free period is time-limited, so recipients who want ongoing protection after the covered year will need to arrange and potentially pay for monitoring themselves.
How this compares with other recent breaches
The DMDC incident fits a familiar pattern: a legacy government or enterprise system holding Social Security numbers in unencrypted form, exposed for months before discovery, followed by a slow trickle of disclosure rather than a single, specific public accounting. It's a similar shape to the breach Pandromeda covered in the IDScan.net driver's-license data exposure, where sensitive identity documents were likewise exposed well before the public learned the full scope.
It's worth noting what this incident is not: reporting so far does not describe it as a classic exploited zero-day vulnerability chased by an external attack group. It's described as unauthorized access to an unencrypted file-sharing system with a security vulnerability — closer to a misconfiguration or access-control failure than the kind of actively-exploited software flaw explained in our zero-day vulnerability explainer. That distinction matters for accountability: this looks like an internal control failure DMDC could plausibly have caught sooner, rather than a novel attack technique nobody could have anticipated.
What affected individuals should do next
If you are a current or former DoD service member, civilian employee, or a dependent of one, and you are unsure whether your data was included, the practical steps are the same regardless of whether you've received a letter yet:
- Watch for and read the DMDC notification letter carefully if one arrives, and enroll in the free IDX credit monitoring and identity-restoration offer before the enrollment window closes.
- Request your free credit reports through AnnualCreditReport.com, the official site mandated by federal law, and check for accounts or inquiries you don't recognize.
- Consider a credit freeze or fraud alert with the three major credit bureaus, which is free and prevents most new accounts from being opened in your name without your explicit action.
- Use a password manager to harden other accounts tied to the exposed contact details, since attackers who obtain a name, birth date and SSN often attempt to pair that with credential-stuffing or phishing against email and financial accounts; our 1Password vs. Dashlane comparison is a reasonable starting point if you don't already use one.
- Report suspected identity theft at the FTC's IdentityTheft.gov, which provides a personalized recovery plan and, for service members specifically, resources summarized by the FTC's military identity-theft guidance, including eligibility for active-duty alerts.
- Be alert to phishing that references this breach specifically — scammers frequently use real breach news as pretext for follow-on phishing emails or calls impersonating "DMDC" or "the Pentagon" asking you to "verify" your SSN or payment details. DMDC will not ask you to confirm your SSN by email or phone in response to this incident.
We will update this article if the Department of Defense issues a public statement, if additional notification details become available, or if evidence of data misuse is confirmed.
Frequently asked questions
What is the Pentagon DMDC data breach?
It's an incident in which unauthorized users accessed an unencrypted file-sharing system belonging to the Defense Manpower Data Center (DMDC), a Pentagon personnel-records agency, from around October 2025 until the vulnerability was discovered and patched on July 16, 2026. A DMDC notification letter dated September 18, 2026 says the exposed files included Social Security numbers and other personal data.
How many people were affected by the Pentagon data breach?
More than 3 million people, according to the notification letter: roughly 2.8 million living current and former service members, civilian employees and dependents, plus about 294,000 deceased former defense personnel or their dependents.
What personal data was exposed in the DMDC breach?
Social Security numbers combined with at least one other identifier, which could include full name, date of birth, contact information, sex, race, or military job/occupational-specialty details. No financial account numbers, passwords, or classified material have been reported as part of the exposure.
Has the Department of Defense officially confirmed this breach?
Not through a public press release. The facts come from a DMDC notification letter sent to affected individuals, which leaked onto Reddit before two defense officials confirmed its authenticity to reporters. When asked directly for more detail, the Department of Defense did not immediately respond, according to Military Times. No statement has appeared on defense.gov as of this writing.
What should I do if I think my data was exposed?
Enroll in the free one-year IDX credit monitoring and identity-restoration offer if you receive a notification letter, pull your free credit reports at AnnualCreditReport.com, consider a credit freeze, and report any suspected identity theft at IdentityTheft.gov. Be cautious of phishing messages that reference this breach.
Is this the same as a hacked zero-day vulnerability?
No. Reporting describes the cause as unauthorized access to an unencrypted file-sharing system with a security vulnerability, which is closer to a misconfiguration or access-control failure than an actively exploited zero-day software flaw.
Sources
- Wikipedia: Defense Manpower Data Centeren.wikipedia.org
- OMB Memorandum M-17-12: Preparing for and Responding to a Breach of Personally Identifiable Informationobamawhitehouse.archives.gov
- FTC: IdentityTheft.govidentitytheft.gov
- FTC Consumer Alert: Military Data Spotlight - Identity Theft and Servicemembersconsumer.ftc.gov
- AnnualCreditReport.com (official federally mandated site)annualcreditreport.com
Sana Qureshi runs the security and privacy desk. She reports on actively exploited vulnerabilities, vendor patches and data breaches, and covers the password managers, VPNs and authentication tools readers use to protect themselves. Her alerts cite vendor advisories, CISA and the CVE record directly.