Samsung October 2026 Security Update Patches 9 Critical Flaws
SMR-OCT-2026 closes nine critical Android CVEs, 33 High and four Samsung Semiconductor flaws across the Galaxy S26, Z Fold8 and Z Flip8 lineups.
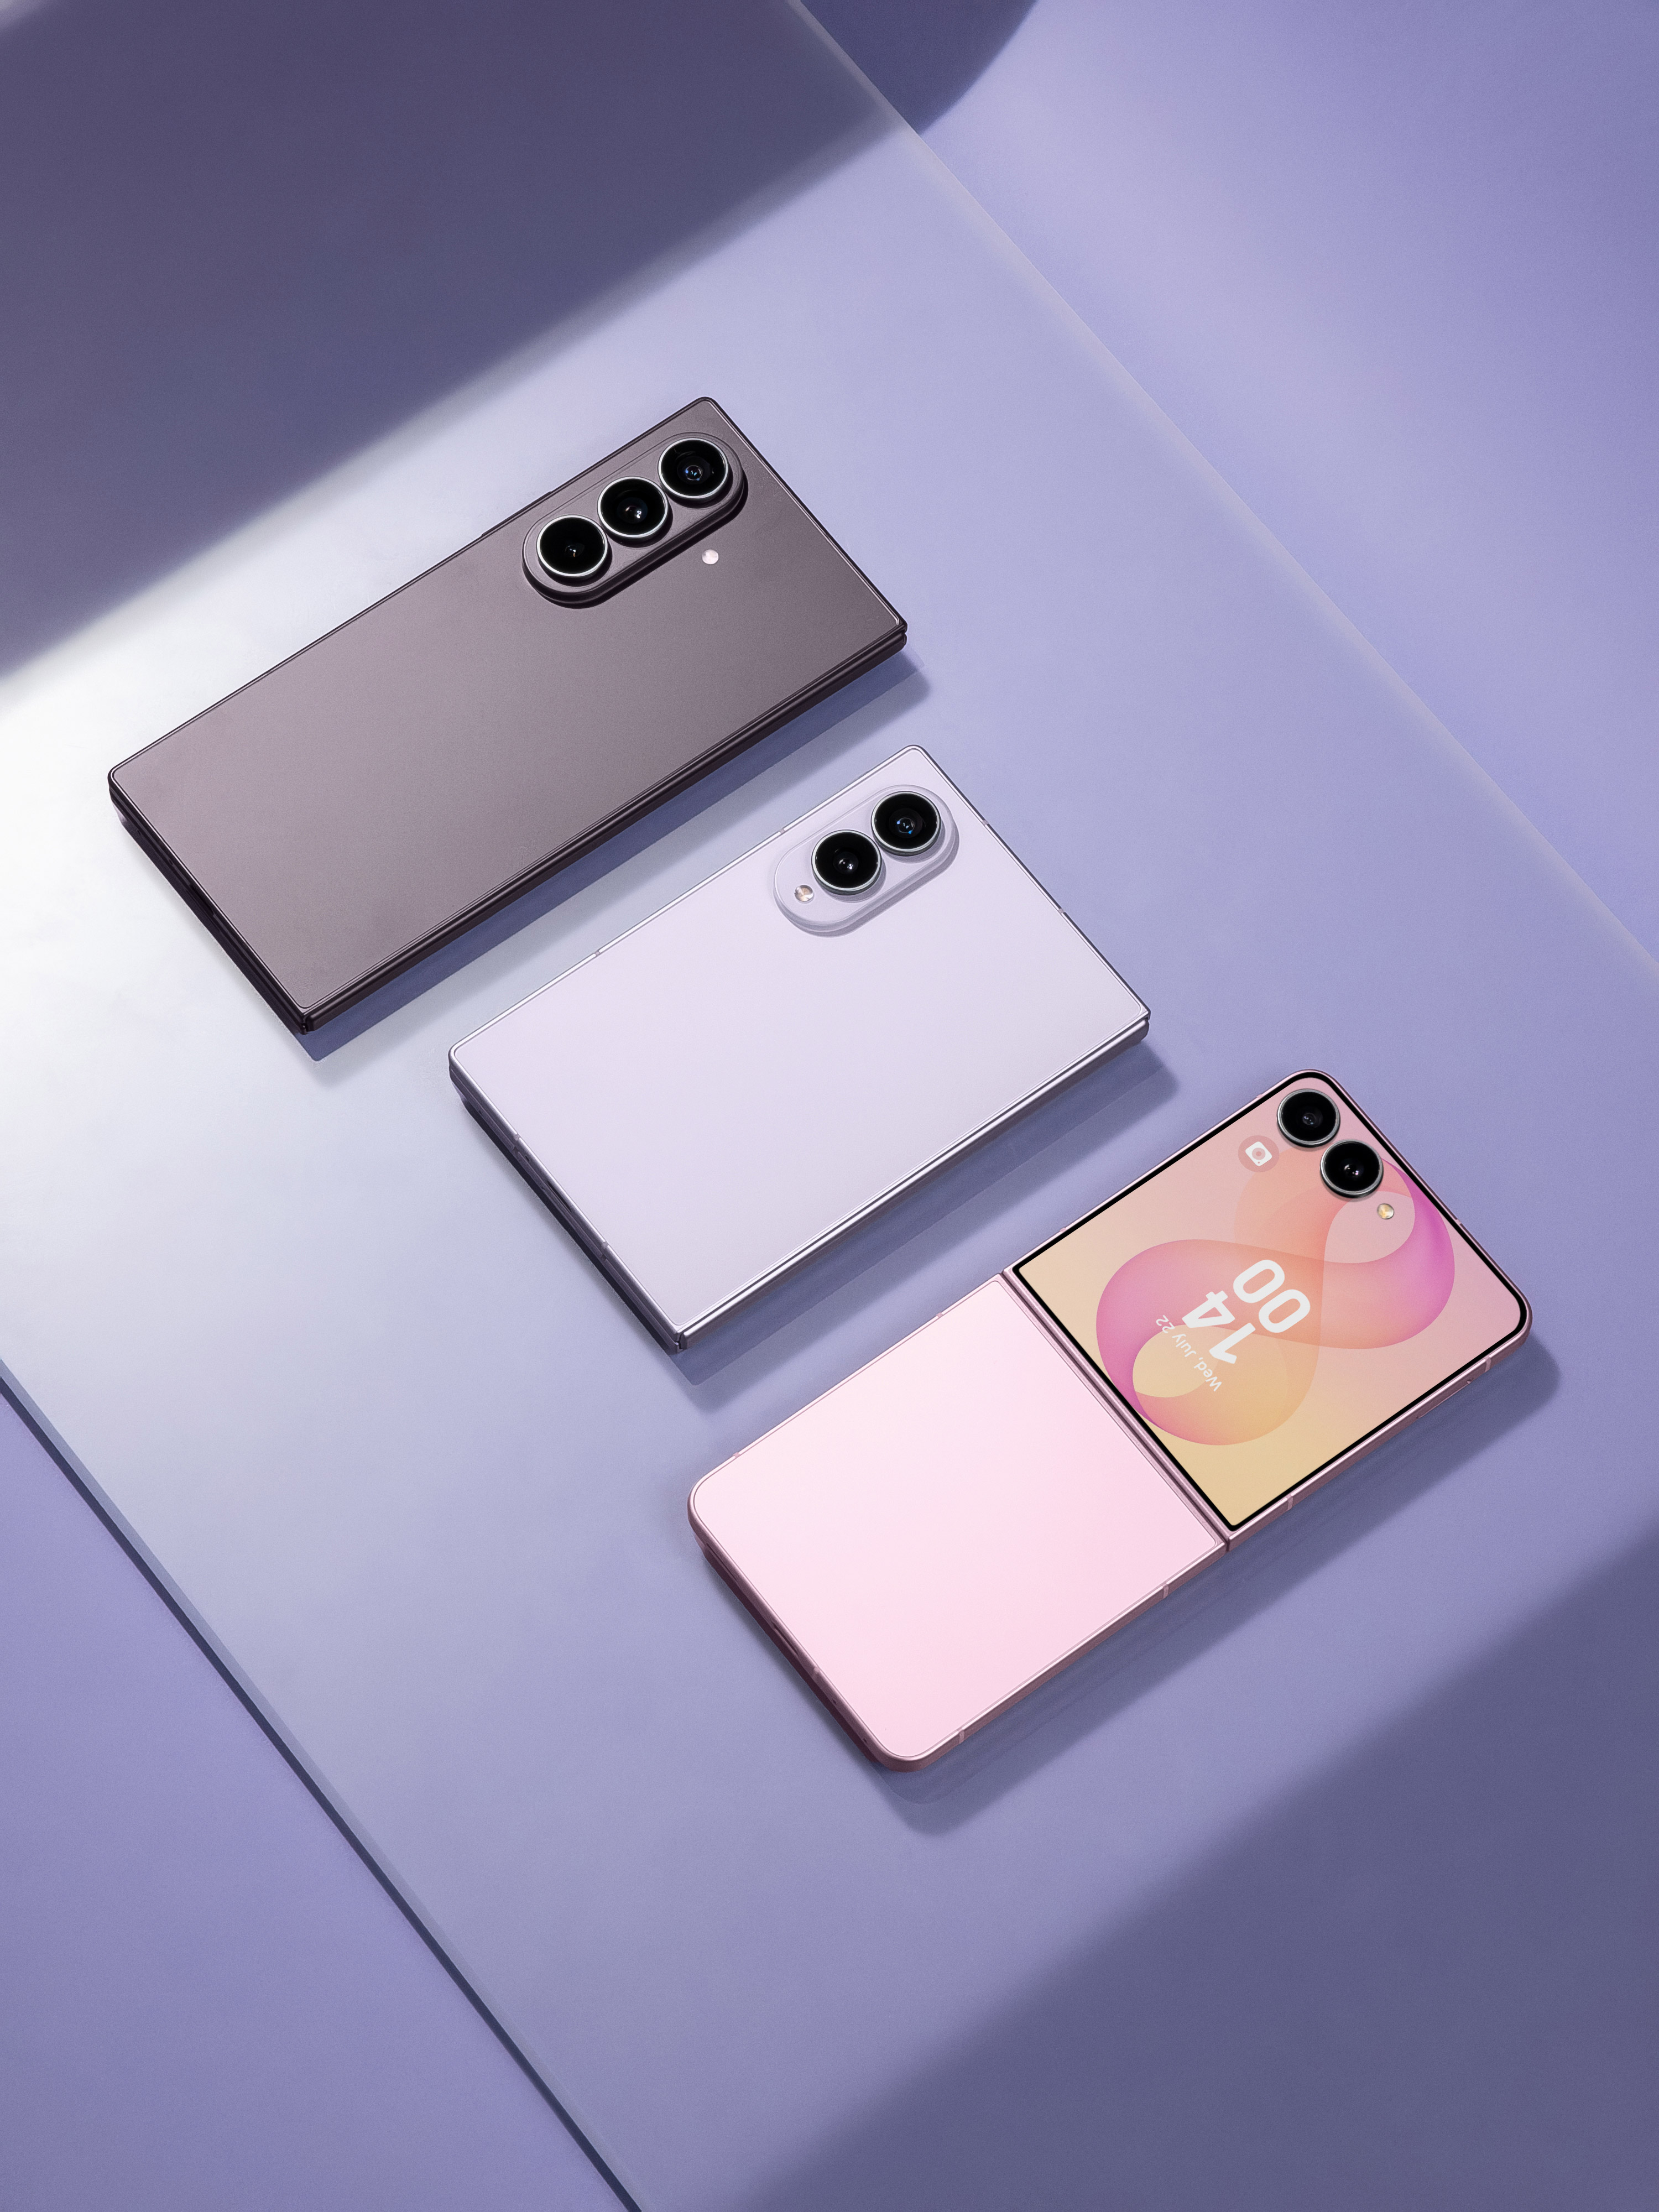
Samsung has released SMR-OCT-2026, its October 2026 Security Maintenance Release, closing out nine critical Android vulnerabilities, 33 rated High and three Moderate from the October Android Security Bulletin, plus four High-severity Samsung Semiconductor flaws and a batch of Samsung-only fixes tracked under the company's own SVE numbering. The update is rolling out now to the Galaxy S26 series, the Galaxy Z Fold8, Z Fold8 Ultra and Z Flip8, and other current-generation Galaxy phones and tablets running One UI. Owners can grab it from Settings > Software update, where it typically lands as a few hundred megabytes depending on model and carrier.
The release mirrors what Google just did for Pixel with its October 2026 Pixel security update, except it is Samsung patching its own Android skin, its Knox security layer and the Exynos and Samsung-made chip components that ship inside Galaxy hardware on top of the upstream Android fixes.
SMR-OCT-2026 at a glance
- Published: October 6, 2026, by Samsung Mobile Security
- Android Security Bulletin CVEs patched: 9 Critical, 33 High, 3 Moderate
- Samsung Semiconductor CVEs: 4, all rated High (CVE-2026-35494, CVE-2026-68993, CVE-2026-69043, CVE-2026-69044)
- Samsung-specific (SVE) items: includes SVE-2026-1758 / CVE-2026-21114, an out-of-bounds write in libsmkvextractor.so that can be used for local code execution
- Devices covered: Galaxy S26 series, Galaxy Z Fold8, Z Fold8 Ultra, Z Flip8, and other current flagship and mid-range Galaxy models on supported One UI versions
- How to get it: Settings > Software update > Download and install
What is SMR-OCT-2026?
SMR stands for Security Maintenance Release, Samsung's name for the monthly (or near-monthly) patch bundle it ships to Galaxy devices. Samsung publishes the full list on its own Samsung Mobile Security update page, where SMR-OCT-2026 is listed with a publish date of October 6, 2026. Each SMR folds together three layers of fixes: the vulnerabilities Google discloses that month in the Android Security Bulletin, patches for Samsung's own semiconductor and modem components, and fixes for issues found exclusively in Samsung's software, which the company tracks under its own SVE (Samsung Vulnerabilities and Exposures) identifiers.
For October, Samsung's bulletin lists 9 Critical, 33 High and 3 Moderate CVEs carried over from the Android Security Bulletin, four additional High-severity Samsung Semiconductor CVEs, and 27 SVE items spanning Samsung's own apps, Knox components and pre-loaded utilities, though Samsung does not publicly disclose the full technical detail on every SVE entry.
The critical CVEs patched this month
Samsung's own count of nine critical issues lines up closely with Google's upstream disclosure. The October 2026 Android Security Bulletin, published by Google on October 5, 2026 and updated October 8, lists 25 vulnerabilities in AOSP code, seven of them Critical: a Framework denial-of-service bug and six issues in the System component, mostly in the Bluetooth stack, that can be chained into local privilege escalation without the attacker needing extra execution privileges or any interaction from the device owner. Samsung's bulletin adds two more Critical entries, CVE-2026-20519 and CVE-2026-20520, that trace back to chipset-level components rather than the core AOSP framework.
The seven CVEs Google itself rates Critical are CVE-2026-58865 (Framework, remote denial of service), CVE-2026-55269, CVE-2026-55280, CVE-2026-58835 and CVE-2026-58880 (System/Bluetooth and NFC, local privilege escalation), and CVE-2026-49933 and CVE-2026-55265 (System, denial of service). None of these were reported as exploited in the wild prior to patching, according to Google's bulletin, but Bluetooth and NFC privilege-escalation bugs are the kind of flaw security researchers watch closely because they can sometimes be triggered with little or no user interaction over a short-range radio connection.
Samsung-specific flaws and semiconductor CVEs
Beyond the Android-wide issues, SMR-OCT-2026 closes four High-severity flaws in Samsung's own semiconductor components, published separately on Samsung Semiconductor's product security updates page: CVE-2026-35494, CVE-2026-68993, CVE-2026-69043 and CVE-2026-69044. These sit below the Android OS layer, in chipset firmware and drivers that Samsung designs itself for use across Galaxy and other devices.
The most notable Samsung-only fix this month is SVE-2026-1758, tracked externally as CVE-2026-21114: an out-of-bounds write in libsmkvextractor.so, a native media-parsing library, that can be abused for local code execution. Because it requires local access or a malicious file being opened on the device rather than a remote network trigger, Samsung rates it High rather than Critical, but it is still the kind of bug that chains well with other exploits in a longer attack sequence, which is exactly the Pwn2Own-style research that has previously targeted Galaxy S26 hardware at live hacking competitions.
Which Galaxy devices are affected
SMR-OCT-2026 is a maintenance release for Samsung's current flagship lineup and the broader set of Galaxy devices still inside their software-support window. That means it covers the Galaxy S26, S26+ and S26 Ultra, the Galaxy Z Fold8, Z Fold8 Ultra and Z Flip8 that Samsung introduced at Galaxy Unpacked in July 2026 and formally launched in August, and extends to the previous-generation Galaxy S25 and Z Fold7/Flip7 families, plus select Galaxy A-series and Tab models, as each device's software-update schedule allows. Samsung's security bulletin does not publish a device-by-device matrix; instead, it states that the fix set applies to "major flagship models" and that actual delivery timing varies by region, carrier and model.
In practice, the newest hardware gets the update first. The Galaxy S26 series was already running One UI 9 on Android 17 when SMR-OCT-2026 began rolling out, and the Z Fold8 lineup picked it up on the same One UI 9 base shortly after. Older devices on earlier Android versions still receive the subset of fixes that applies to their software, which is why the Android Security Bulletin's per-version tables matter as much as Samsung's headline CVE count.
Galaxy S26 rollout timeline
Samsung pushed SMR-OCT-2026 to the Galaxy S26 series in stages. The update began reaching S26 units in Europe in late September, shortly after the stable One UI 9 release, and carrier and regional firmware listings have shown it landing under build numbers such as S948BXXS4BZIG in Europe. US and Canadian S26 owners started seeing the same patch level in early October, with regional firmware builds reported in the S948U1UES4BZIG and S948WVLS4BZIG range. As with any staged Samsung rollout, availability depends on carrier approval, so two S26 units on different networks can show different update dates even in the same country. Samsung's own One UI 9 rollout tracker for the S26 series is the better reference than any single build number for checking where a specific carrier variant stands.
Galaxy Z Fold8 and Z Flip8 rollout
The Z Fold8 Ultra, Z Fold8 and Z Flip8 launched already running One UI 9, which Samsung has said bundles roughly 79 security-related improvements on top of the stock Android base the foldables ship with. SMR-OCT-2026 layers the October Android Security Bulletin fixes and the Samsung-specific SVE patches on top of that One UI 9 foundation, so Z Fold8 and Z Flip8 owners who are current on their One UI update are also current on this month's security patch level. As with the S26 series, exact delivery dates vary by carrier and region, and Samsung recommends checking Settings > Software update directly on the device rather than relying on a fixed calendar date.
| Device family | Software base | SMR-OCT-2026 status (as of Oct 15, 2026) |
|---|---|---|
| Galaxy S26 / S26+ / S26 Ultra | One UI 9 (Android 17) | Rolling out since late September (EU), early October (US/Canada) |
| Galaxy Z Fold8 / Z Fold8 Ultra | One UI 9 (Android 17) | Rolling out, following the Z Fold8 launch build |
| Galaxy Z Flip8 | One UI 9 (Android 17) | Rolling out alongside the Z Fold8 lineup |
| Galaxy S25 / S25+ / S25 Ultra | One UI 9 (Android 17) | Expected in the following weeks, per Samsung's staged schedule |
| Galaxy Z Fold7 / Z Flip7 | One UI 8 or One UI 9 | Expected in the following weeks, device- and carrier-dependent |
How Samsung tracks its own vulnerabilities
The CVE system, run through the National Vulnerability Database, is the common language for vulnerabilities across the entire tech industry, but Samsung also keeps a parallel internal log called SVE, for Samsung Vulnerabilities and Exposures. An SVE number gets assigned to a bug found in Samsung's own code, whether that's a pre-loaded app, a Knox security module, or a native library like libsmkvextractor.so, the component behind this month's SVE-2026-1758. Some SVE entries eventually get a matching public CVE identifier, as SVE-2026-1758 did when it was cross-referenced to CVE-2026-21114; others stay internal if Samsung judges that publishing technical detail would make the bug easier to exploit before most devices are patched.
Samsung Knox, the security platform baked into every modern Galaxy device, sits underneath this patch process rather than being patched independently. Knox enforces the hardware root of trust and app-level sandboxing that limits what an attacker can do even after exploiting one of this month's CVEs, which is part of why Samsung treats most of the Samsung-only SVE entries as High severity rather than Critical: a successful exploit still has to get past Knox's additional containment before it can do serious damage on a fully updated device.
How this compares to Google's Pixel update
Samsung and Google both draw on the same upstream Android Security Bulletin, so the core AOSP-level fixes in SMR-OCT-2026 are the same ones Google shipped to Pixel phones this month. The difference is everything layered on top: Samsung has to patch Knox, its own One UI framework code, Samsung Semiconductor's chip components, and a long tail of pre-installed Samsung apps, which is why Samsung's CVE count runs higher than a Pixel-only bulletin and why Samsung's rollout, spread across dozens of carriers and device tiers worldwide, takes noticeably longer to reach every eligible phone than Google's single-vendor Pixel rollout does.
How to update your Galaxy phone
On any supported Galaxy device, open Settings, scroll to Software update, and tap Download and install. If SMR-OCT-2026 hasn't reached your region or carrier yet, the device will report that it's already running the latest available software, since updates roll out in waves rather than all at once. Samsung's security bulletin page lists the current SMR level for reference, and checking it against the build number under Settings > About phone > Software information is the most reliable way to confirm a specific device is current.
Why monthly patches like this matter
None of the CVEs closed in SMR-OCT-2026 were flagged by Google or Samsung as actively exploited before the patch shipped, but several of the Critical entries, particularly the Bluetooth and NFC privilege-escalation bugs, are the type of flaw that security researchers have previously demonstrated in live conditions. Security competitions such as Pwn2Own have repeatedly shown that current Galaxy flagships, S26 included, can be broken into by chaining together exactly this kind of OS-level and chip-level bug, which is why Samsung and Google both treat the monthly patch cycle as a baseline rather than optional maintenance.
What to do next
Galaxy S26, Z Fold8, Z Fold8 Ultra and Z Flip8 owners should open Settings > Software update today and install SMR-OCT-2026 if it has reached their device; if it hasn't, it is worth checking again over the next week as Samsung's staged carrier rollout continues. Owners of older Galaxy S25, Z Fold7 and Z Flip7 hardware should expect the same patch set in the following weeks and can confirm their current SMR level any time by comparing the build number in Settings > About phone against Samsung's published bulletin. There is no workaround or mitigation Samsung has published for any of these CVEs short of installing the update itself, since none require configuration changes to exploit.
Frequently asked questions
What is SMR-OCT-2026?
SMR-OCT-2026 is Samsung's October 2026 Security Maintenance Release, published October 6, 2026. It bundles fixes for 9 Critical, 33 High and 3 Moderate CVEs from the October Android Security Bulletin, 4 High-severity Samsung Semiconductor CVEs, and a set of Samsung-only fixes tracked under its internal SVE numbering.
Which Galaxy devices get the October 2026 security update?
Samsung is rolling SMR-OCT-2026 out to the Galaxy S26, S26+ and S26 Ultra, the Galaxy Z Fold8, Z Fold8 Ultra and Z Flip8, and extending it to the Galaxy S25 and Z Fold7/Flip7 families and other current Galaxy phones and tablets as each device's update schedule allows.
How many critical vulnerabilities does SMR-OCT-2026 fix?
Samsung's bulletin lists 9 Critical CVEs this month. Seven come directly from Google's October 2026 Android Security Bulletin; two more, CVE-2026-20519 and CVE-2026-20520, are chipset-level issues Samsung adds on top of the AOSP list.
Were any of the patched vulnerabilities exploited before the fix?
No. Neither Google's October 2026 Android Security Bulletin nor Samsung's SMR-OCT-2026 bulletin lists any of this month's CVEs as exploited in the wild prior to patching.
How do I check if my Galaxy phone has SMR-OCT-2026 installed?
Open Settings, then Software update, and tap Download and install to check for the latest patch. You can confirm the exact build under Settings > About phone > Software information and compare it against Samsung's published security bulletin.
When will the Galaxy S25 and other older Galaxy phones get this update?
Samsung rolls SMR patches out in stages, newest flagships first. S26 and Z Fold8/Flip8 series devices received SMR-OCT-2026 first, in late September and October; older models such as the Galaxy S25 and Z Fold7/Flip7 are expected to follow in the following weeks, timing depending on carrier and region.
Sources
- Samsung Mobile Security - SMR-OCT-2026 bulletinsecurity.samsungmobile.com
- Android Security Bulletin - October 2026source.android.com
- Samsung Semiconductor - Product Security Updatessemiconductor.samsung.com
- Samsung Newsroom - Galaxy Z Fold8 Ultra, Fold8 and Flip8 launchnews.samsung.com
- Samsung - Galaxy S26 official product pagesamsung.com
- Samsung - Galaxy Z Fold8 official product pagesamsung.com
Nadia Osei covers mobile and consumer gadgets for Pandromeda: smartphones, tablets, smartwatches, earbuds and smart-home devices. She tracks launches, software updates and pricing across Apple, Google, Samsung and the rest, and builds comparisons from the manufacturers' published specifications.